Compliance · International & Privacy
ISMS evidence that never goes stale.
ISO 27001 certification is won in the surveillance audits, not the ceremony. TriNetra keeps your Annex A control evidence, testing records, and exposure monitoring continuously current — so every audit finds the ISMS actually running.
The regulation
What ISO 27001 expects of you.
ISO/IEC 27001:2022 certifies that an organization runs a functioning Information Security Management System — not just that controls exist on paper, but that they're operated, reviewed, and improved on a defined cycle. Certification bodies expect evidence against Annex A's control set, a documented risk assessment methodology, internal audits, and a management review cycle, verified through certification and periodic surveillance audits between full recertifications. The structural weakness in how most organizations pursue ISO 27001 is timing: controls get tightened up in the weeks before an audit, the auditor checks a point-in-time snapshot, and enforcement relaxes until the next cycle. A control that passed in March and quietly drifted by June is invisible until the next audit finds it — by which point it may have been broken for months. That gap is exactly what turns a compliant organization into a breached one between certification cycles.
How TriNetra maps to it
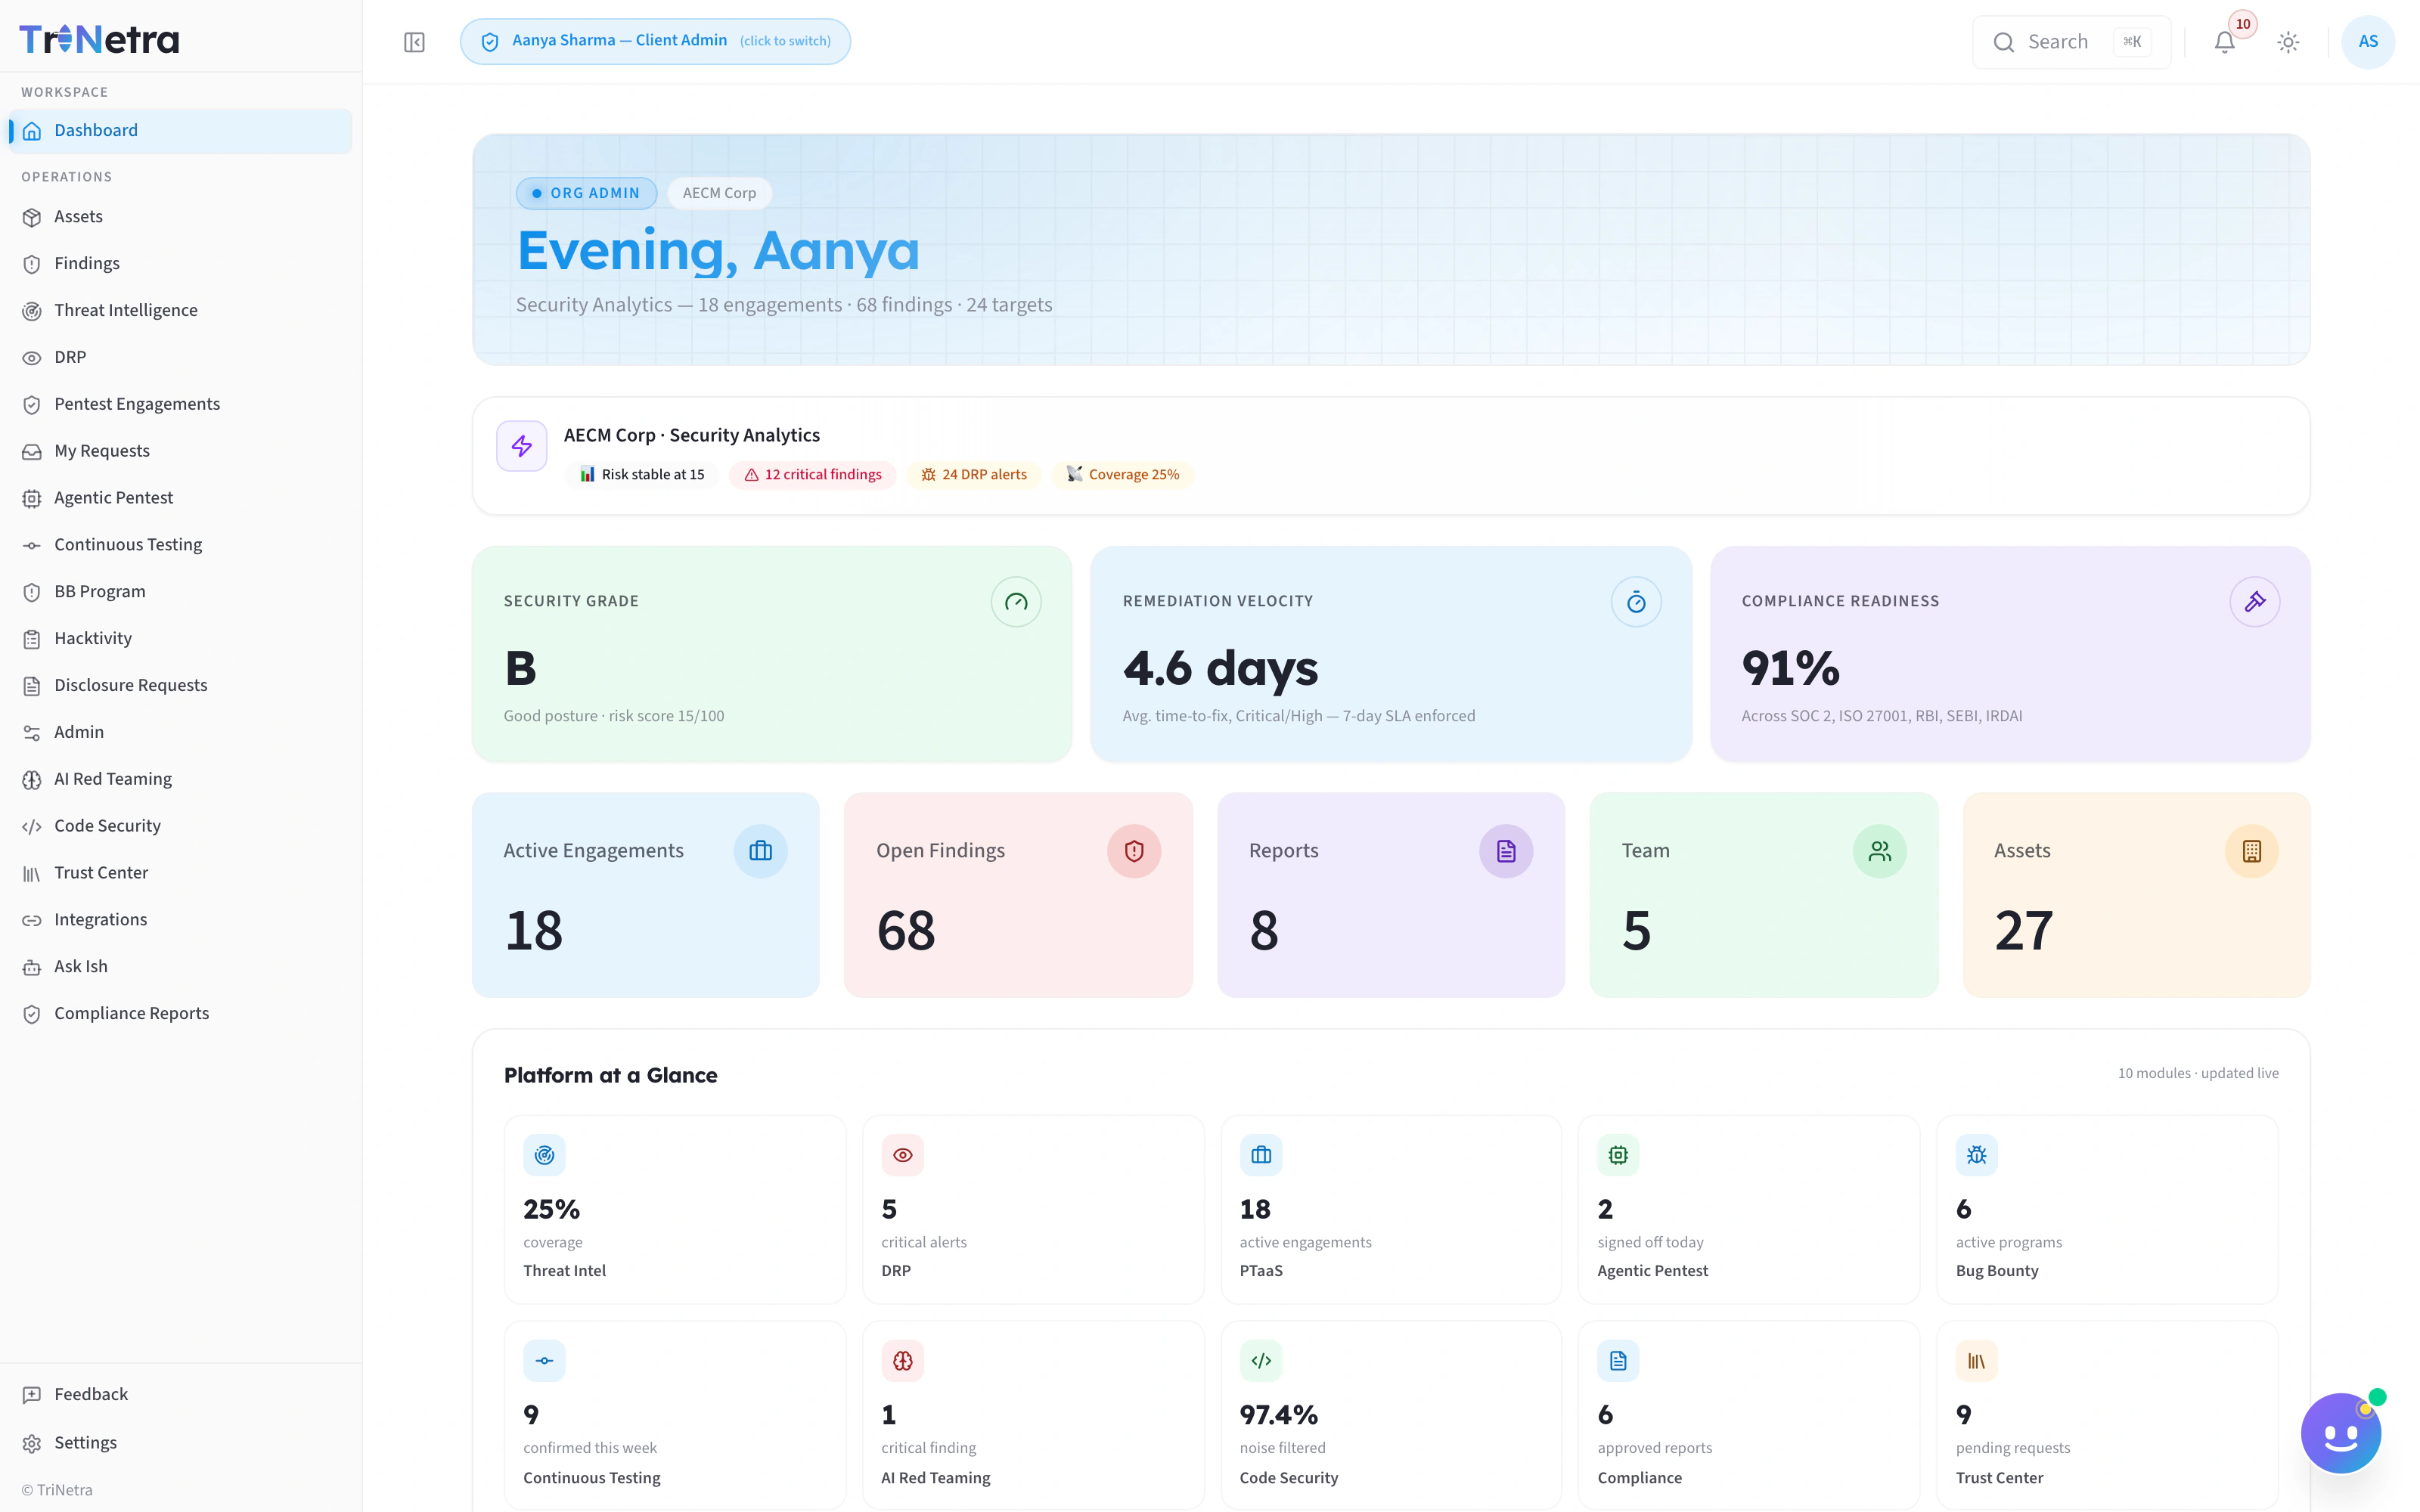
Annex A, evidenced automatically.
| TriNetra module | Evidence produced |
|---|---|
| Continuous Controls Validation | Controls tested on a recurring schedule — as frequent as hourly for connected cloud and identity systems — with full trend history (stable, drifting, or failing) instead of a once-a-year snapshot. When an engineer disables MFA on a service account to debug an integration and forgets to re-enable it, the next scheduled test run catches it, assigns it to a named owner, and updates the evidence trail automatically once it's fixed. |
| PTaaS + Continuous Testing | Technical vulnerability management — recurring pentests with ISO 27001-aligned reporting, plus exploit-confirmed continuous validation between cycles: findings prioritized by real exploitability, closed through a verified retest loop. |
| Attack Surface Management | Asset management and exposure control — a continuously maintained inventory of every internet-facing asset, including the shadow IT your ISMS asset register doesn't know about, with misconfiguration findings mapped to ISO 27001. |
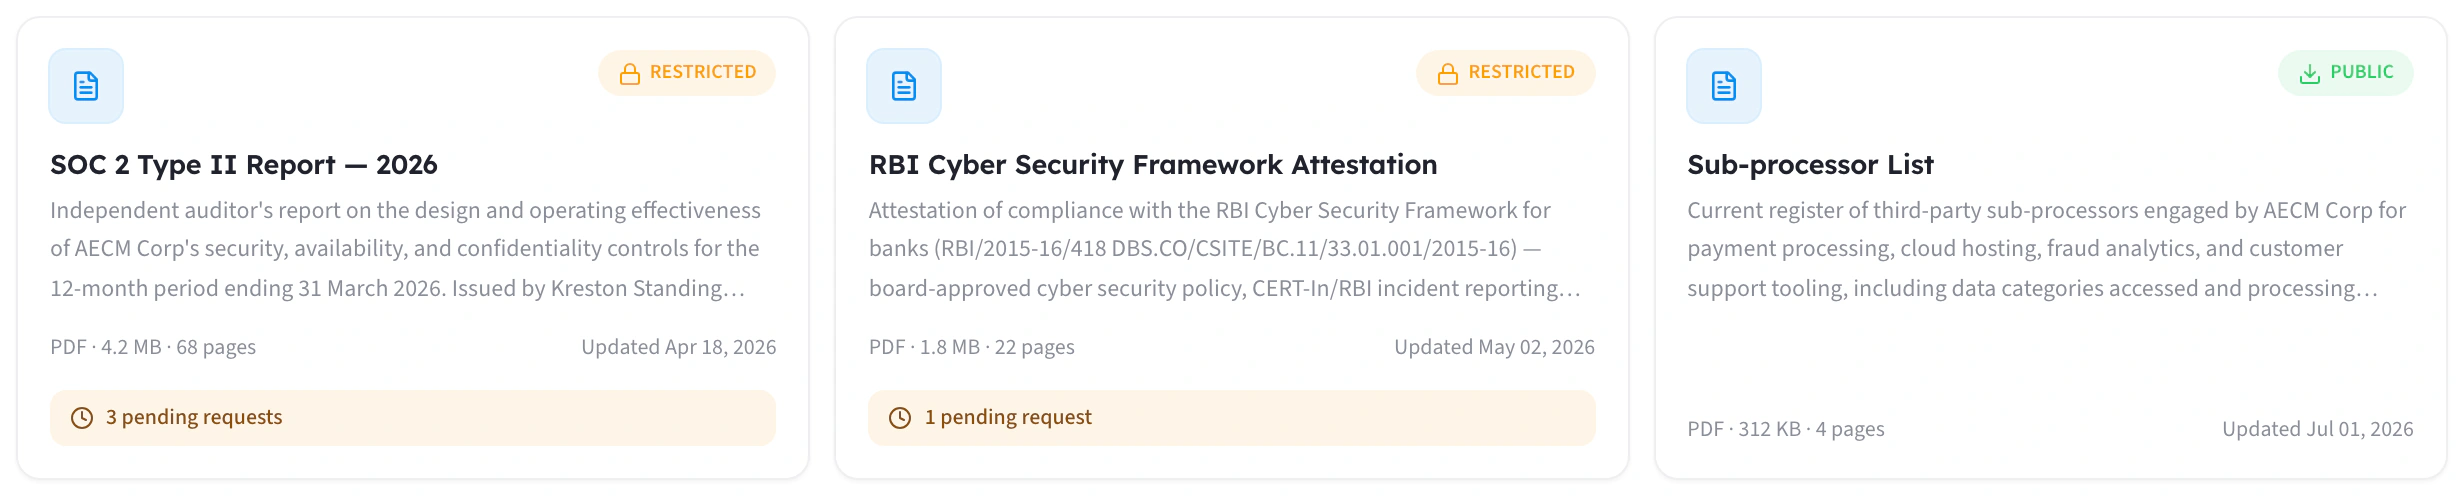
| Trust Center | Your ISO 27001:2022 Certificate and Cloud Addendum variant live as real, gated documents in the Trust Center's library — shared by approval, every access logged, so evidencing your ISMS to customers stops consuming your security team's week. |
| Ish | Management review inputs — ask what changed since the last review (new criticals, control trends, exposure drift) and get an answer grounded in live platform data across every module. |
Keep evidence current between audits with Continuous Controls Validation.
Why SecurityBoat
We hold the certificate we help you keep.
SecurityBoat is ISO 27001 certified ourselves — alongside ISO 9001, SOC 2 Type 2, CERT-In empanelment, and CREST membership. We know what surveillance auditors ask for because we answer the same questions.
Walk into surveillance audits already ready.
Bring your Statement of Applicability. We'll map it to the modules that keep each control's evidence current, automatically.
Let's Connect