Solutions · Enterprise
Built for organizations that can't afford blind spots.
TriNetra gives large and regulated organizations one governed platform for offensive testing, exposure management, and compliance evidence — with the onboarding, account team, and paperwork discipline your procurement process expects from day one.
The enterprise bundle
Six modules. One enterprise-scale narrative.
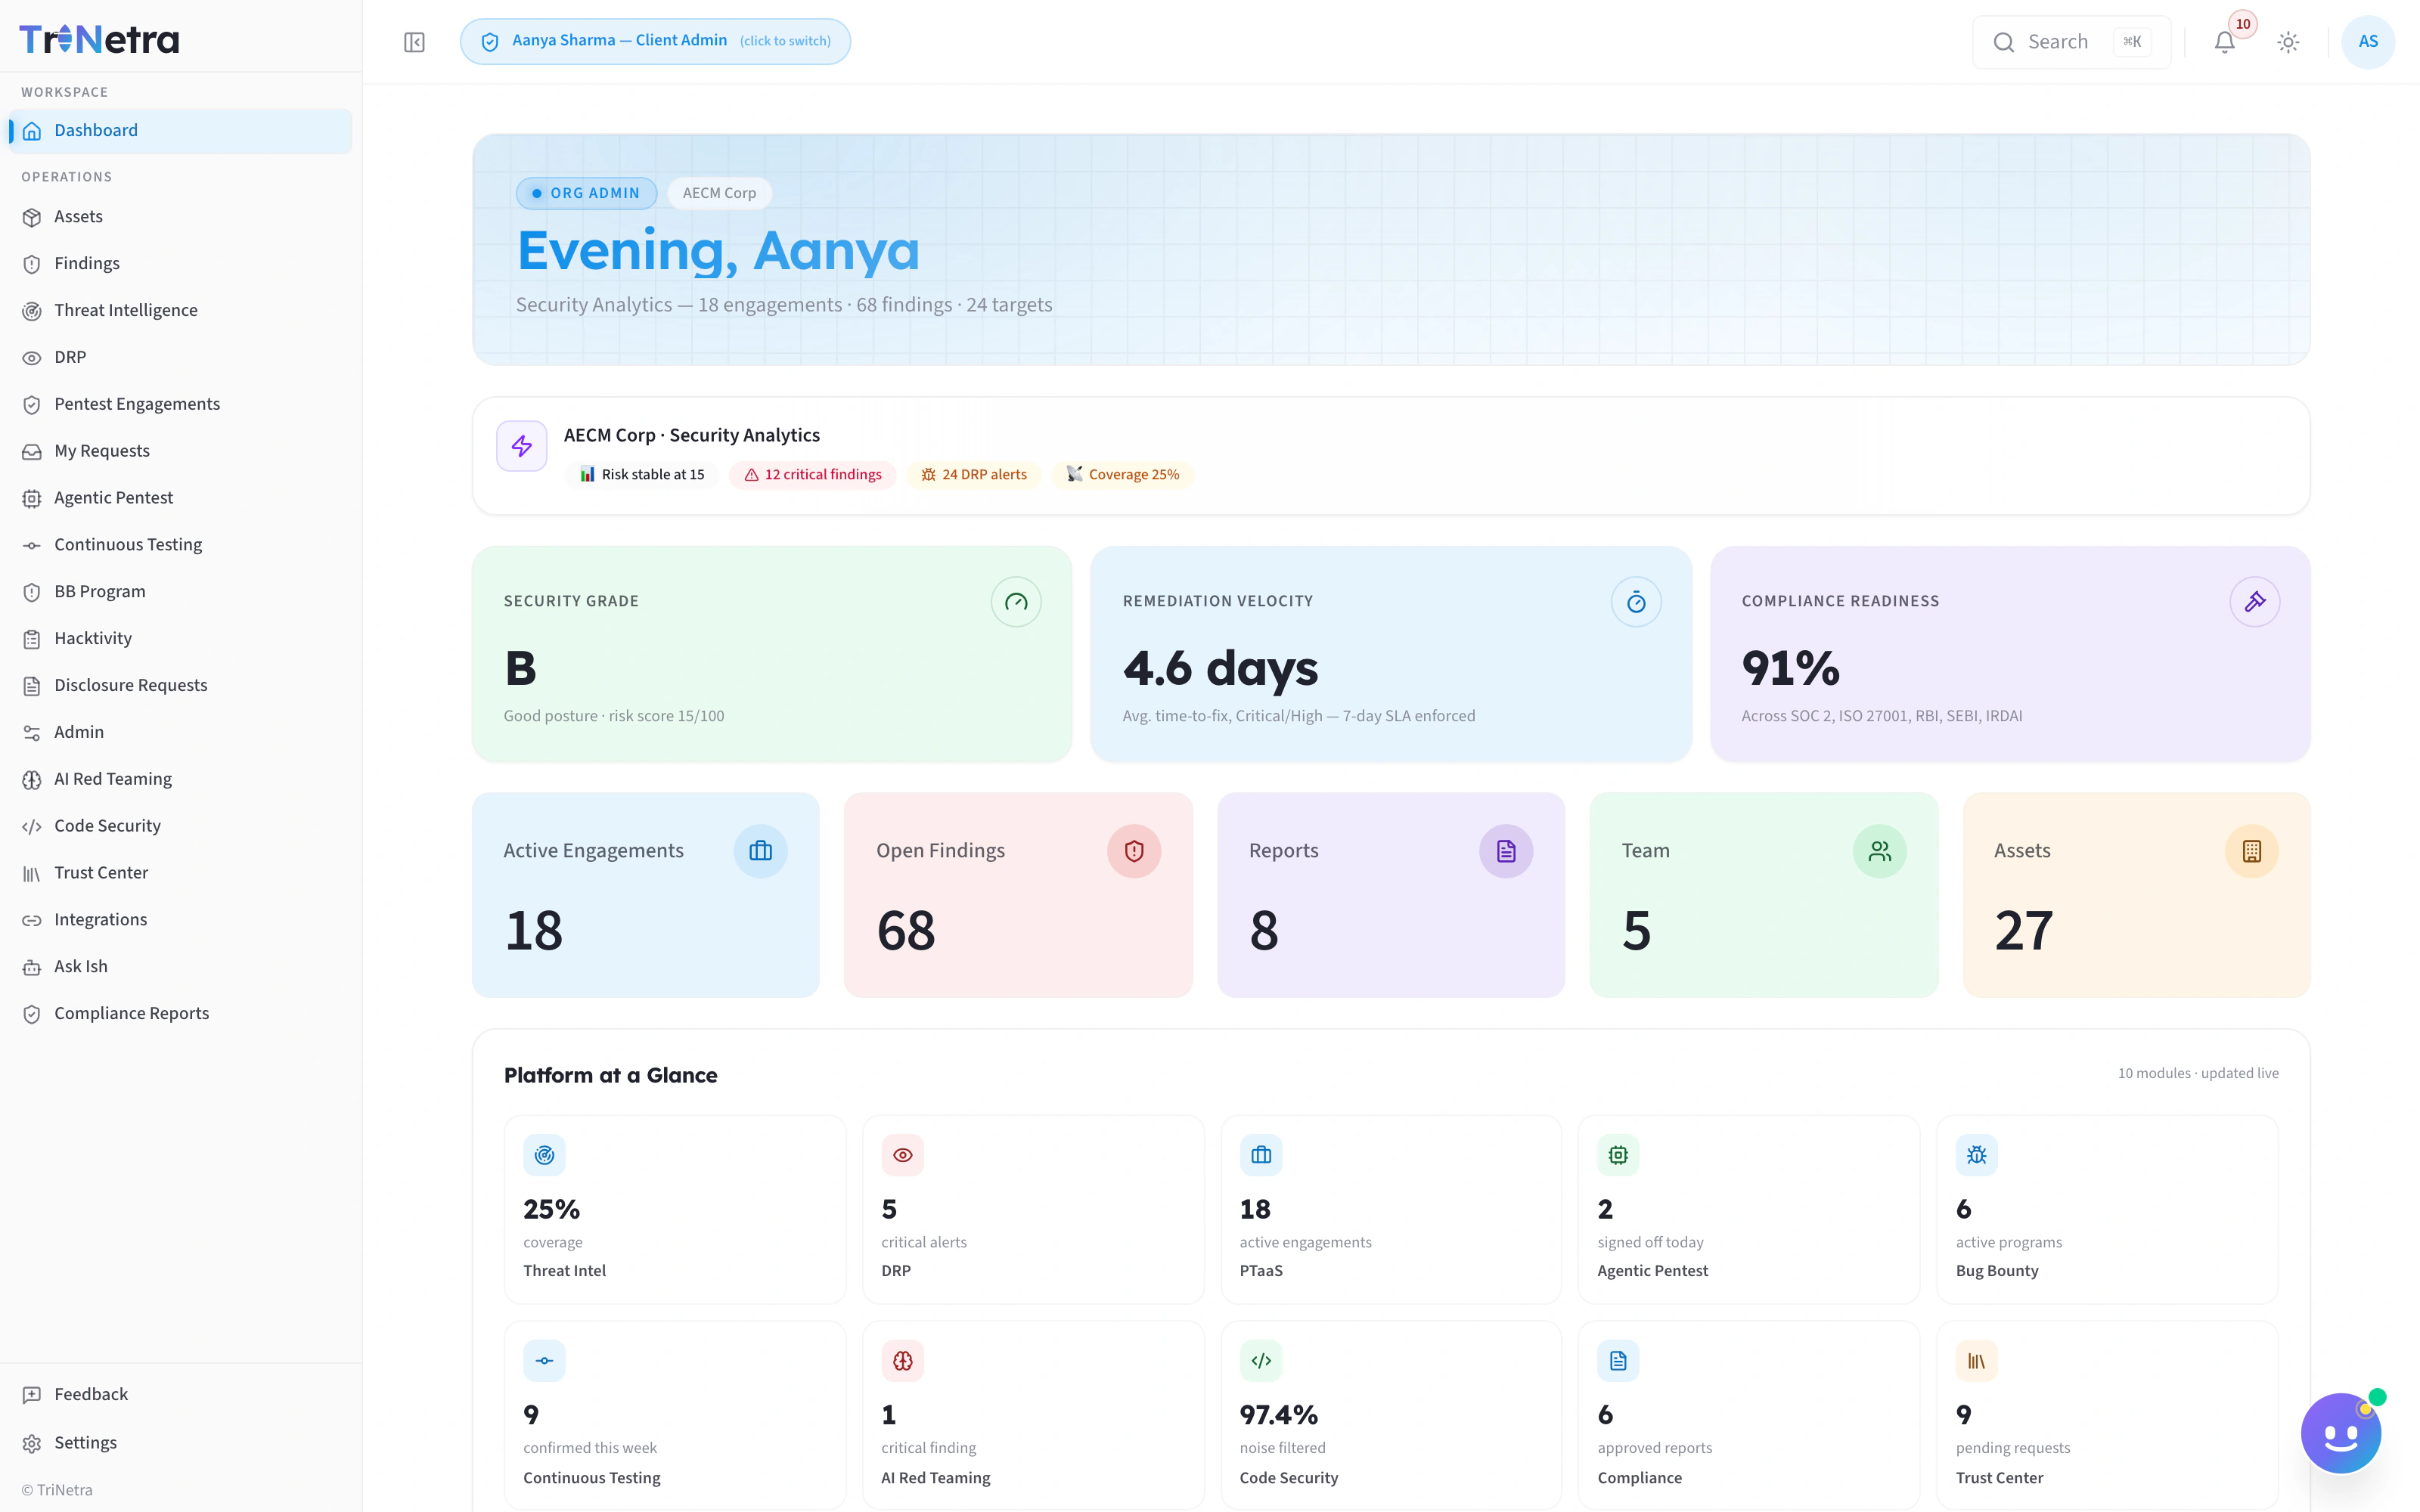
The enterprise deployment of TriNetra bundles the modules large organizations run together — continuous discovery feeding continuous testing, with governance evidence generated from the same live record, and senior security leadership on tap.
| Module | Role in the bundle |
|---|---|
| PTaaS | Compliance-grade pentesting on a recurring cadence — 12-state engagement lifecycle, live findings, enforced retest loop, approved-only reports. |
| Agentic Pentest | AI agents handle reconnaissance at scale; certified humans validate and sign off. Testing frequency keeps pace with your release velocity. |
| Attack Surface Management | Continuous discovery of everything internet-reachable across domains, IPs, and 15+ cloud providers — including the assets a subsidiary forgot to mention. |
| Continuous Controls Validation | Regulatory VAPT reporting generated from live assessment data — SEBI CSCRF and IRDAI report formats shipped end-to-end, white-labelled where needed. |
| Digital Risk Protection | Watches the landscape outside your walls — phishing clones with visual proof, look-alike domains, ransomware leak-site mentions, leaked credentials. |
| vCISO as a Service | Senior security leadership without the single-hire risk — GRC direction, security assessment, and managed security pillars, engaged as a service. |
Incident Response is available alongside the bundle for active breach engagement — paired with DRP's monitoring so response starts from evidence, not from zero.
Rollout & onboarding
One platform, every business unit, no chaos.
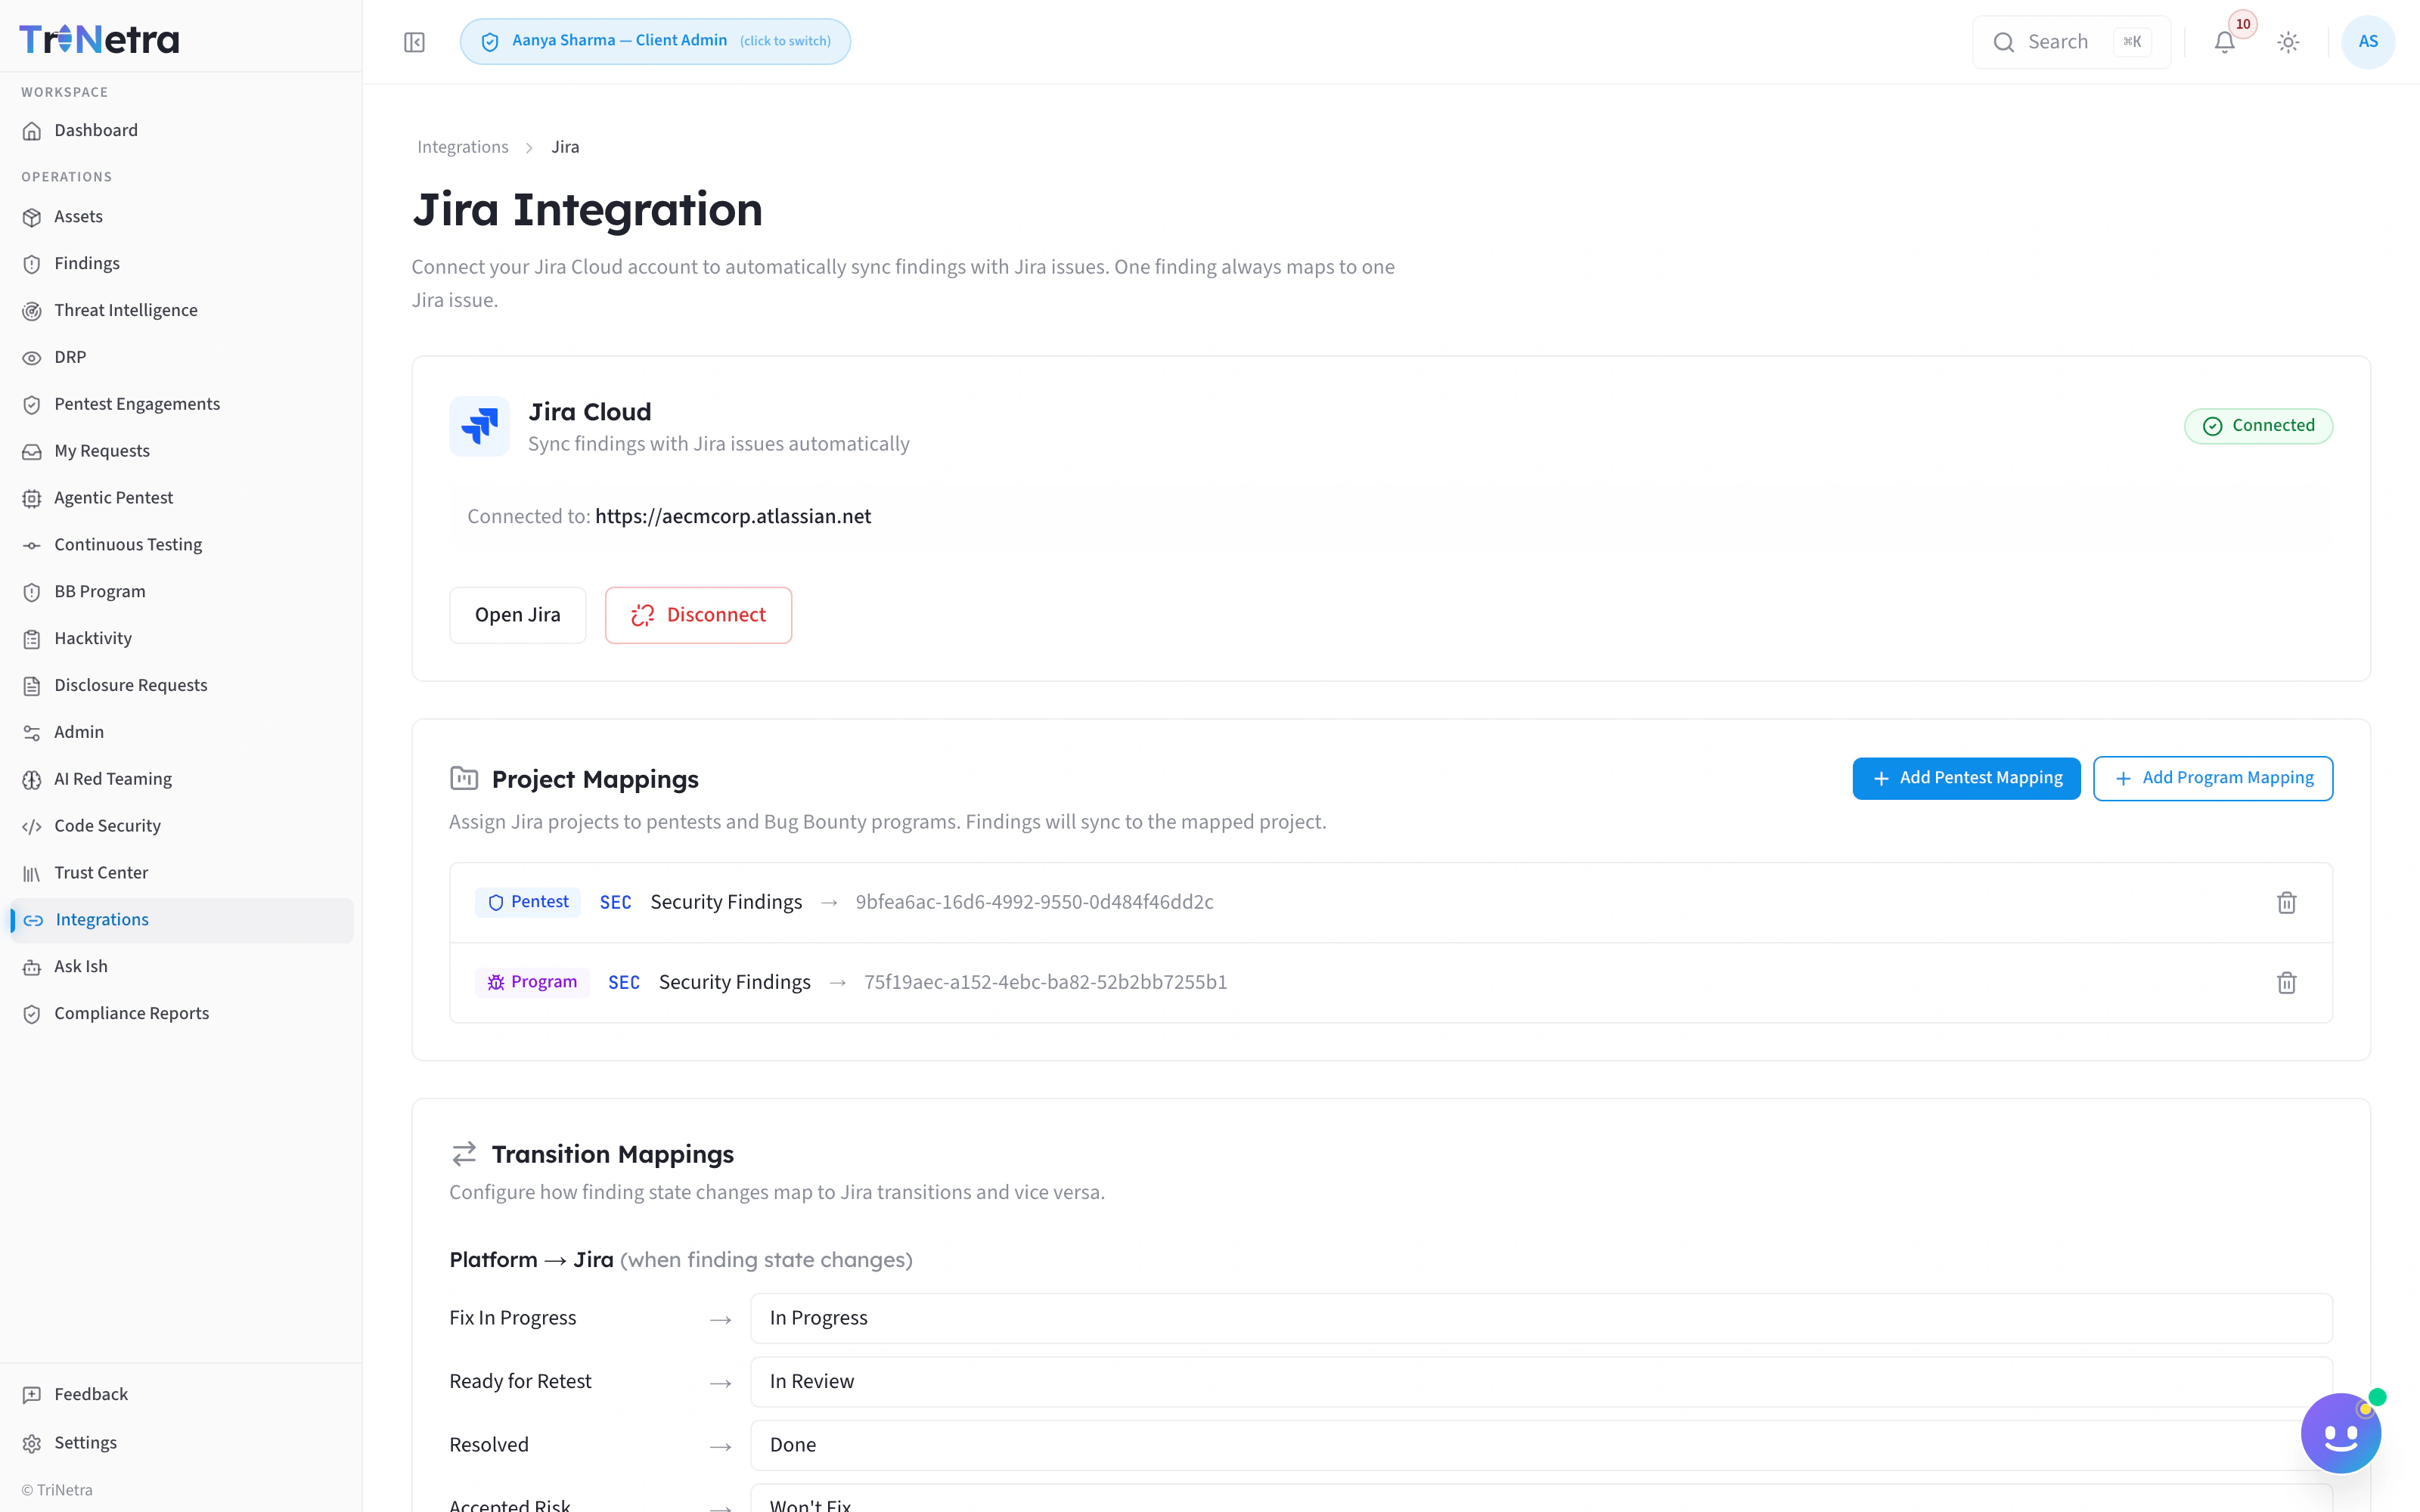
Enterprises don't roll out security tooling to one team — they roll it out to a bank and its broking arm, a parent and its acquisitions, an IT function and forty product squads. TriNetra is built for that shape: scope is bound to a real asset inventory per organization, findings are strictly tenant-scoped, reports are approval-gated before anyone outside the security team sees them, and access is role-scoped throughout. Onboard business units in waves, keep central visibility across all of them, and let each unit see only what belongs to it.
Scoped by design
Governed reporting
Your tools, not new ones
Dedicated account team
A named team, not a ticket queue.
Enterprise customers get dedicated onboarding and a named account team — engagement leads who know your environment, researchers matched to your technology stack, and a direct line when something needs judgment rather than a form. The same continuity carries across pentest cycles, so cycle three starts from cycle two's context instead of from scratch.
Procurement-ready
The paperwork is already done.
SecurityBoat is CERT-In empanelled, a CREST Member, and certified to ISO 27001, ISO 9001, and SOC 2 Type 2 — the credentials your vendor-risk review asks for on page one. For regulated buyers, TriNetra's compliance coverage spans Indian regulatory frameworks (RBI, SEBI CSCRF, IRDAI, CERT-In, NPCI/UPI and more) and international standards (SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR). And if procurement requires an approved reseller, our channel partners have you covered.
SecurityBoat's certifications

Proof
Trusted where the stakes are highest.
- 100+
- organizations secured
- 1,000+
- penetration tests delivered
- 8,000+
- vulnerabilities validated & fixed
- 24/7
- agentic monitoring
“Ninad and his young team are enthusiastic, professional and are fully aware of the implications of their work… Their detailed report and handholding are invaluable.”
Bring us your org chart. We'll bring the platform.
Tell us how your business units are structured and what you're protecting. We'll map a rollout — and show you TriNetra live on your own scope.
Let's Connect