TriNetra · Offensive Testing
Agents map the surface. Humans sign off on every finding.
A coordinated swarm of AI agents runs reconnaissance and exploit-chaining around the clock; certified human testers direct the work, review everything that surfaces, and sign off before anything reaches you as a finding. Same engagement lifecycle and dashboard as PTaaS — at a cadence a human-only team can't sustain.
The problem
Attack surface grows faster than tester headcount. Double your assets and you need roughly double the tester-hours — but budgets and skilled-pentester availability don't scale that way, so testing frequency stalls exactly when release velocity, and risk, are climbing.
How Agentic Pentest answers it
Agentic Pentest changes the cost curve of frequency without changing who's accountable. The product frames this as two things at once — Attacker-Speed Coverage and AI-Native Engineering Resilience — with certified humans directing the swarm and validating every result before it counts.
How it actually works
Four fixed engagement tiers, scoped up front
Gap Assessment
A fast, focused read on one system — where most teams start.
Focused Cycle
Deep coverage of a single product, sustained over a full cycle.
Multi-System
Coordinated coverage across several applications at once.
Full-Stack
Organization-wide surface, tested on a continuous rhythm.
Agents work at the pace an actual attacker would — recon and exploit-chaining running continuously, not on a scheduled scan window.
Your engineering org gets tested at the rate it actually ships, not the rate a human-only team can staff.
Live Recon
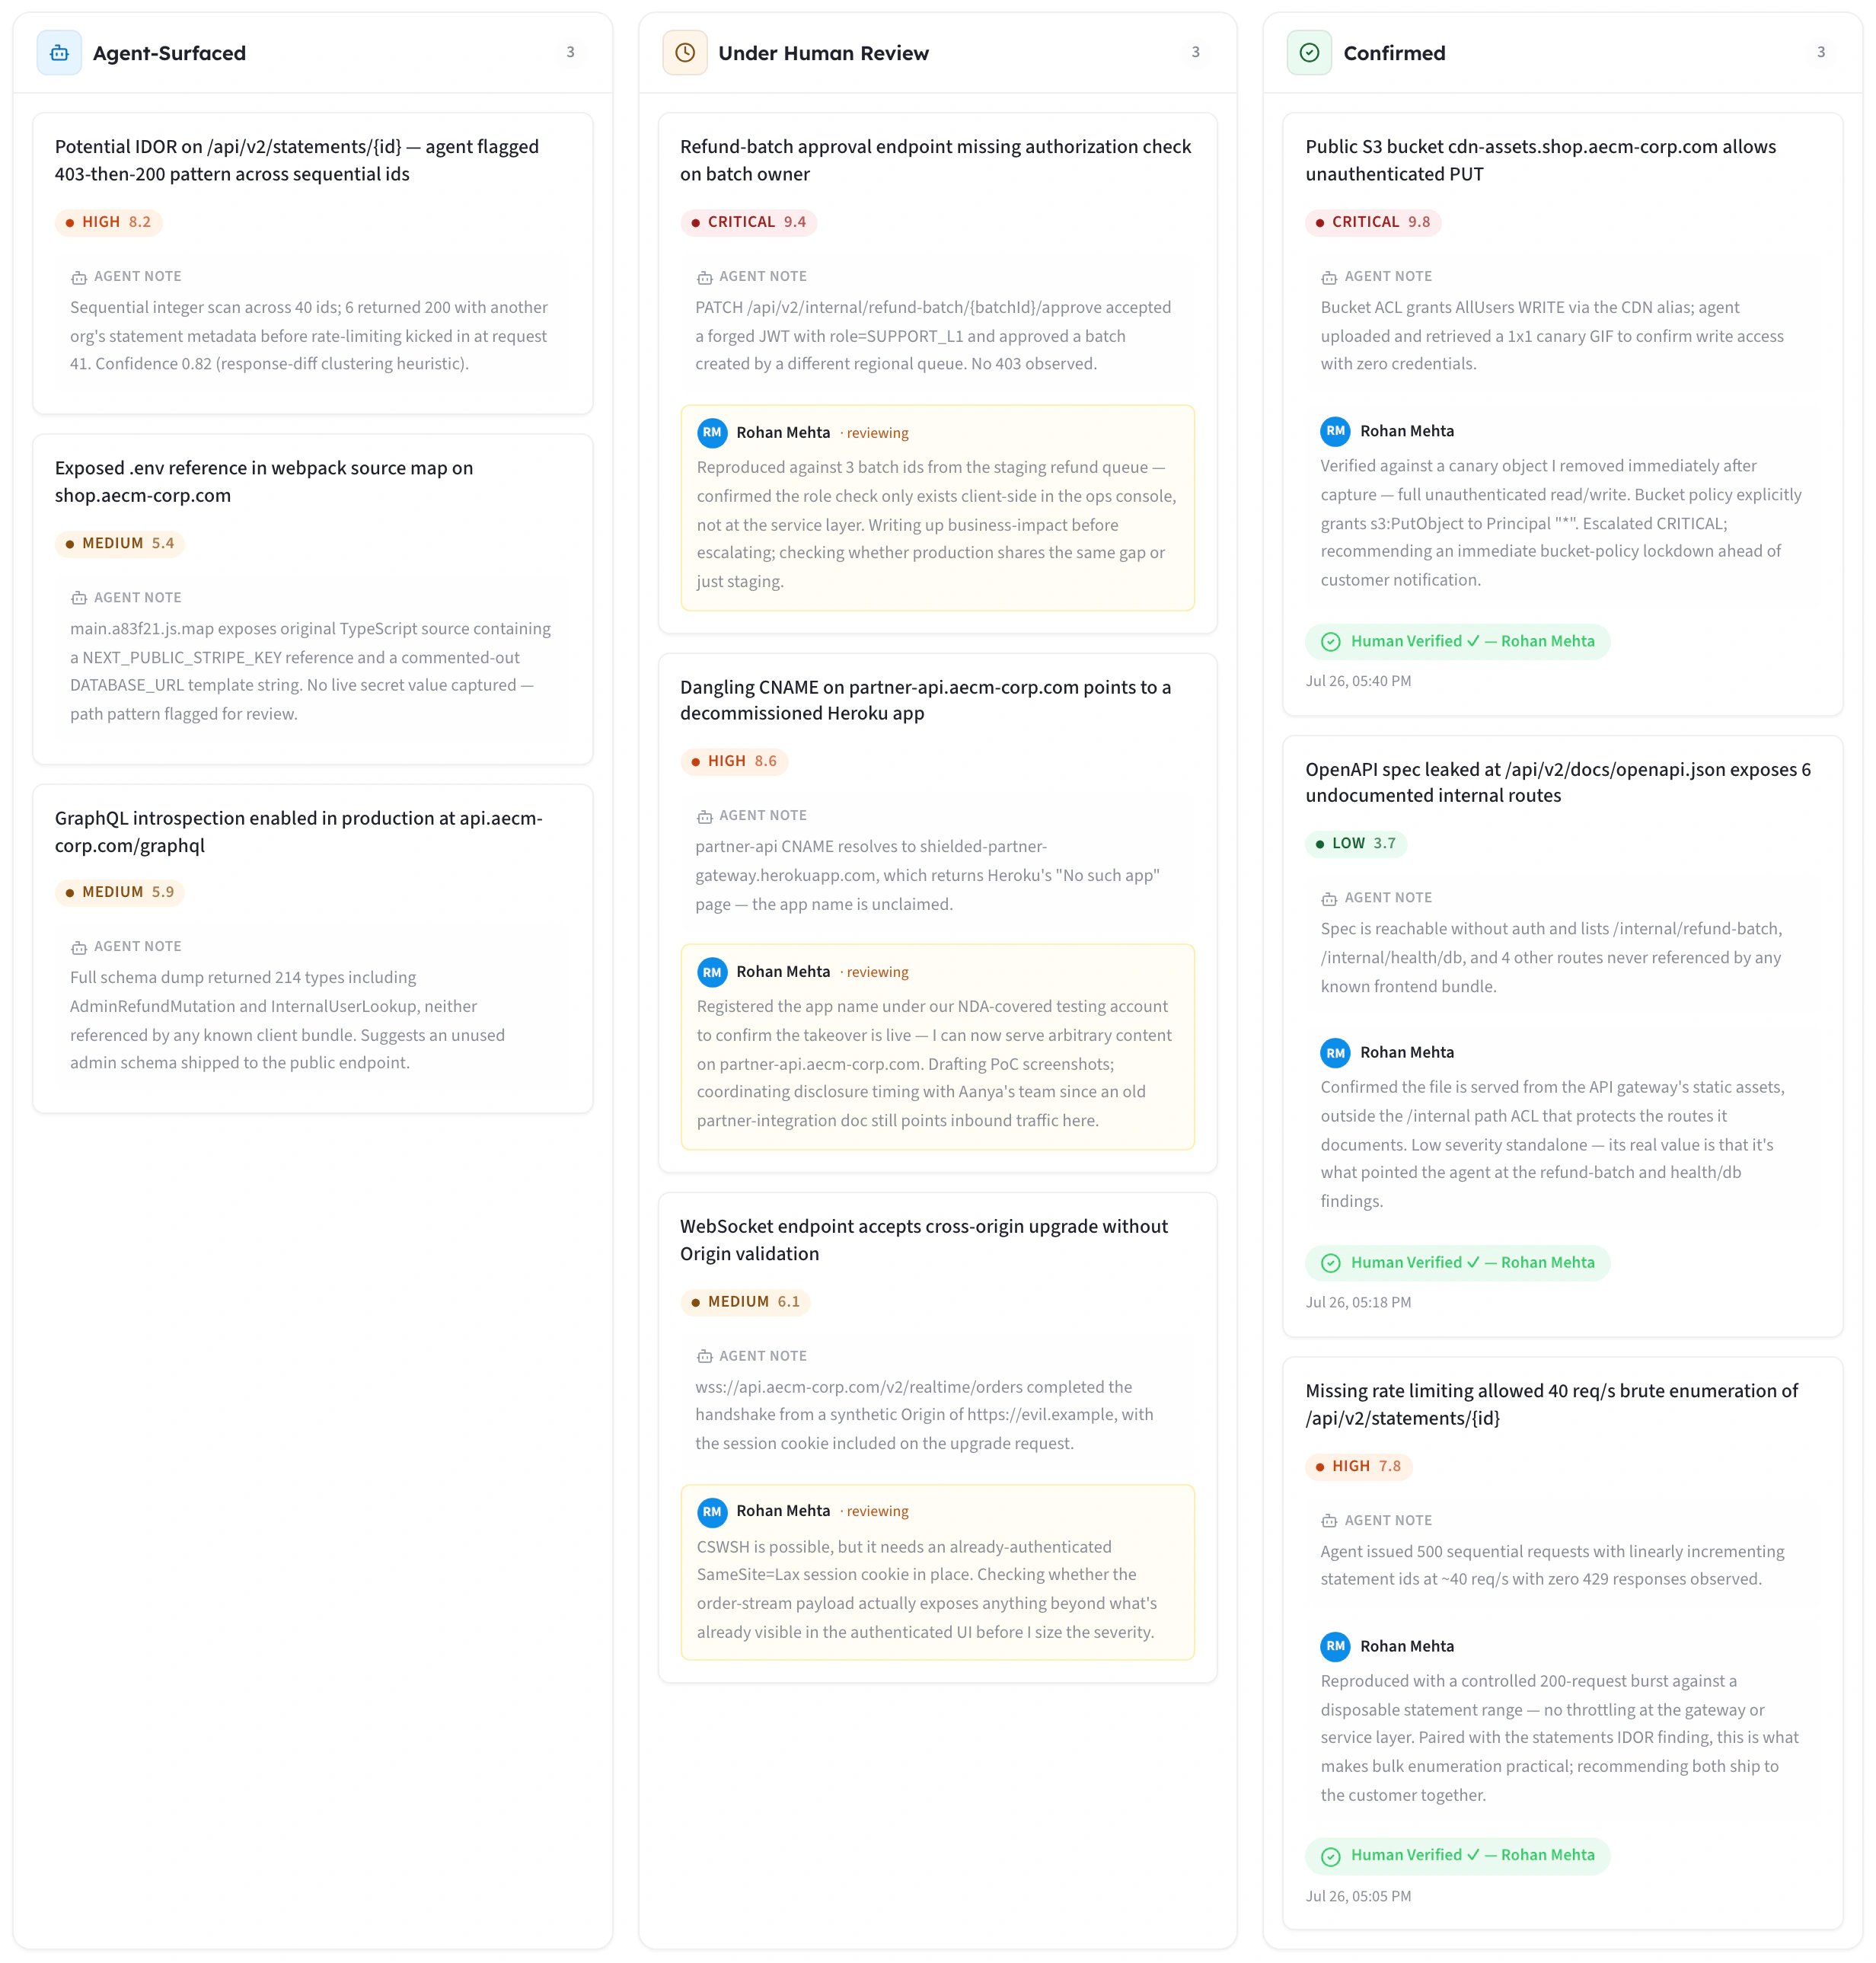
The Human Review Queue
The Sign-Off Log
| Finding | Validated by | Evidence |
|---|---|---|
| Potential IDOR on /api/v2/statements/{id}HIGH · CVSS 8.2 | Certified human tester | Sequential-ID scan reproduced across 6 of 40 IDs before rate-limiting kicked in; confidence 0.82 via response-diff clustering. |
| Refund-batch approval endpoint missing authorization checkCRITICAL · CVSS 9.4 | Rohan Mehta | Reproduced against 3 batch IDs from the staging refund queue — the role check exists client-side only, not enforced at the service layer. |
| Public cloud storage bucket allows unauthenticated PUT requestsCRITICAL · CVSS 9.8 | Certified human tester | Confirmed write access to a storefront CDN asset bucket with no auth header required; escalated for immediate fix. |
Capabilities
What ships in the box
Agent swarm, human command
Live Recon feed
The Human Review Queue
The Sign-Off Log
Four fixed engagement tiers
Same rails as PTaaS
Works with
Stronger together
PTaaS
Attack Surface Management
Ish
Continuous Testing
FAQ
Common questions
Do the AI agents act on their own?
They recon and chain exploit paths continuously under the direction of certified human testers. Nothing becomes a finding until it moves from Agent-Surfaced through Under Human Review to Confirmed in the queue — and every Confirmed finding is logged in the Sign-Off Log with who validated it and on what evidence.
Isn't this just an automated scanner?
No. A scanner emits unverified alerts and stops at pattern-matching. Here, agents do the high-volume discovery and chaining work at attacker speed, and a human makes every judgment call about what's real — direction, validation, and sign-off.
How is this different from regular PTaaS?
Same intake, same 12-state lifecycle, same dashboard, same retest loop — but the swarm runs recon and exploit-chaining continuously through Live Recon, so human testers spend their hours reviewing the Human Review Queue instead of starting discovery from zero.
Which engagement tier should we start with?
Most teams start with the Gap Assessment on one system, then step up to a Focused Cycle or Multi-System engagement as coverage needs grow. Full-Stack suits organizations ready to test their whole surface on a continuous rhythm. We'll help you pick on the first call.
Test at the speed you ship.
Tell us how fast your attack surface is growing. We'll show you what a swarm — with certified humans signing off on every result — can cover before your next release.
Related: PTaaS · Attack Surface Management · Ish · Continuous Testing