SecurityBoat Researchers
Hunt where your work gets paid, not filed.
Join SecurityBoat's vetted researcher community and hunt on real programs through TriNetra — where every submission gets a fair triage, every accepted finding earns severity-scored reputation, and every payout runs on rails, not promises.
Why hunt here
Built by people who submit reports, not just read them.
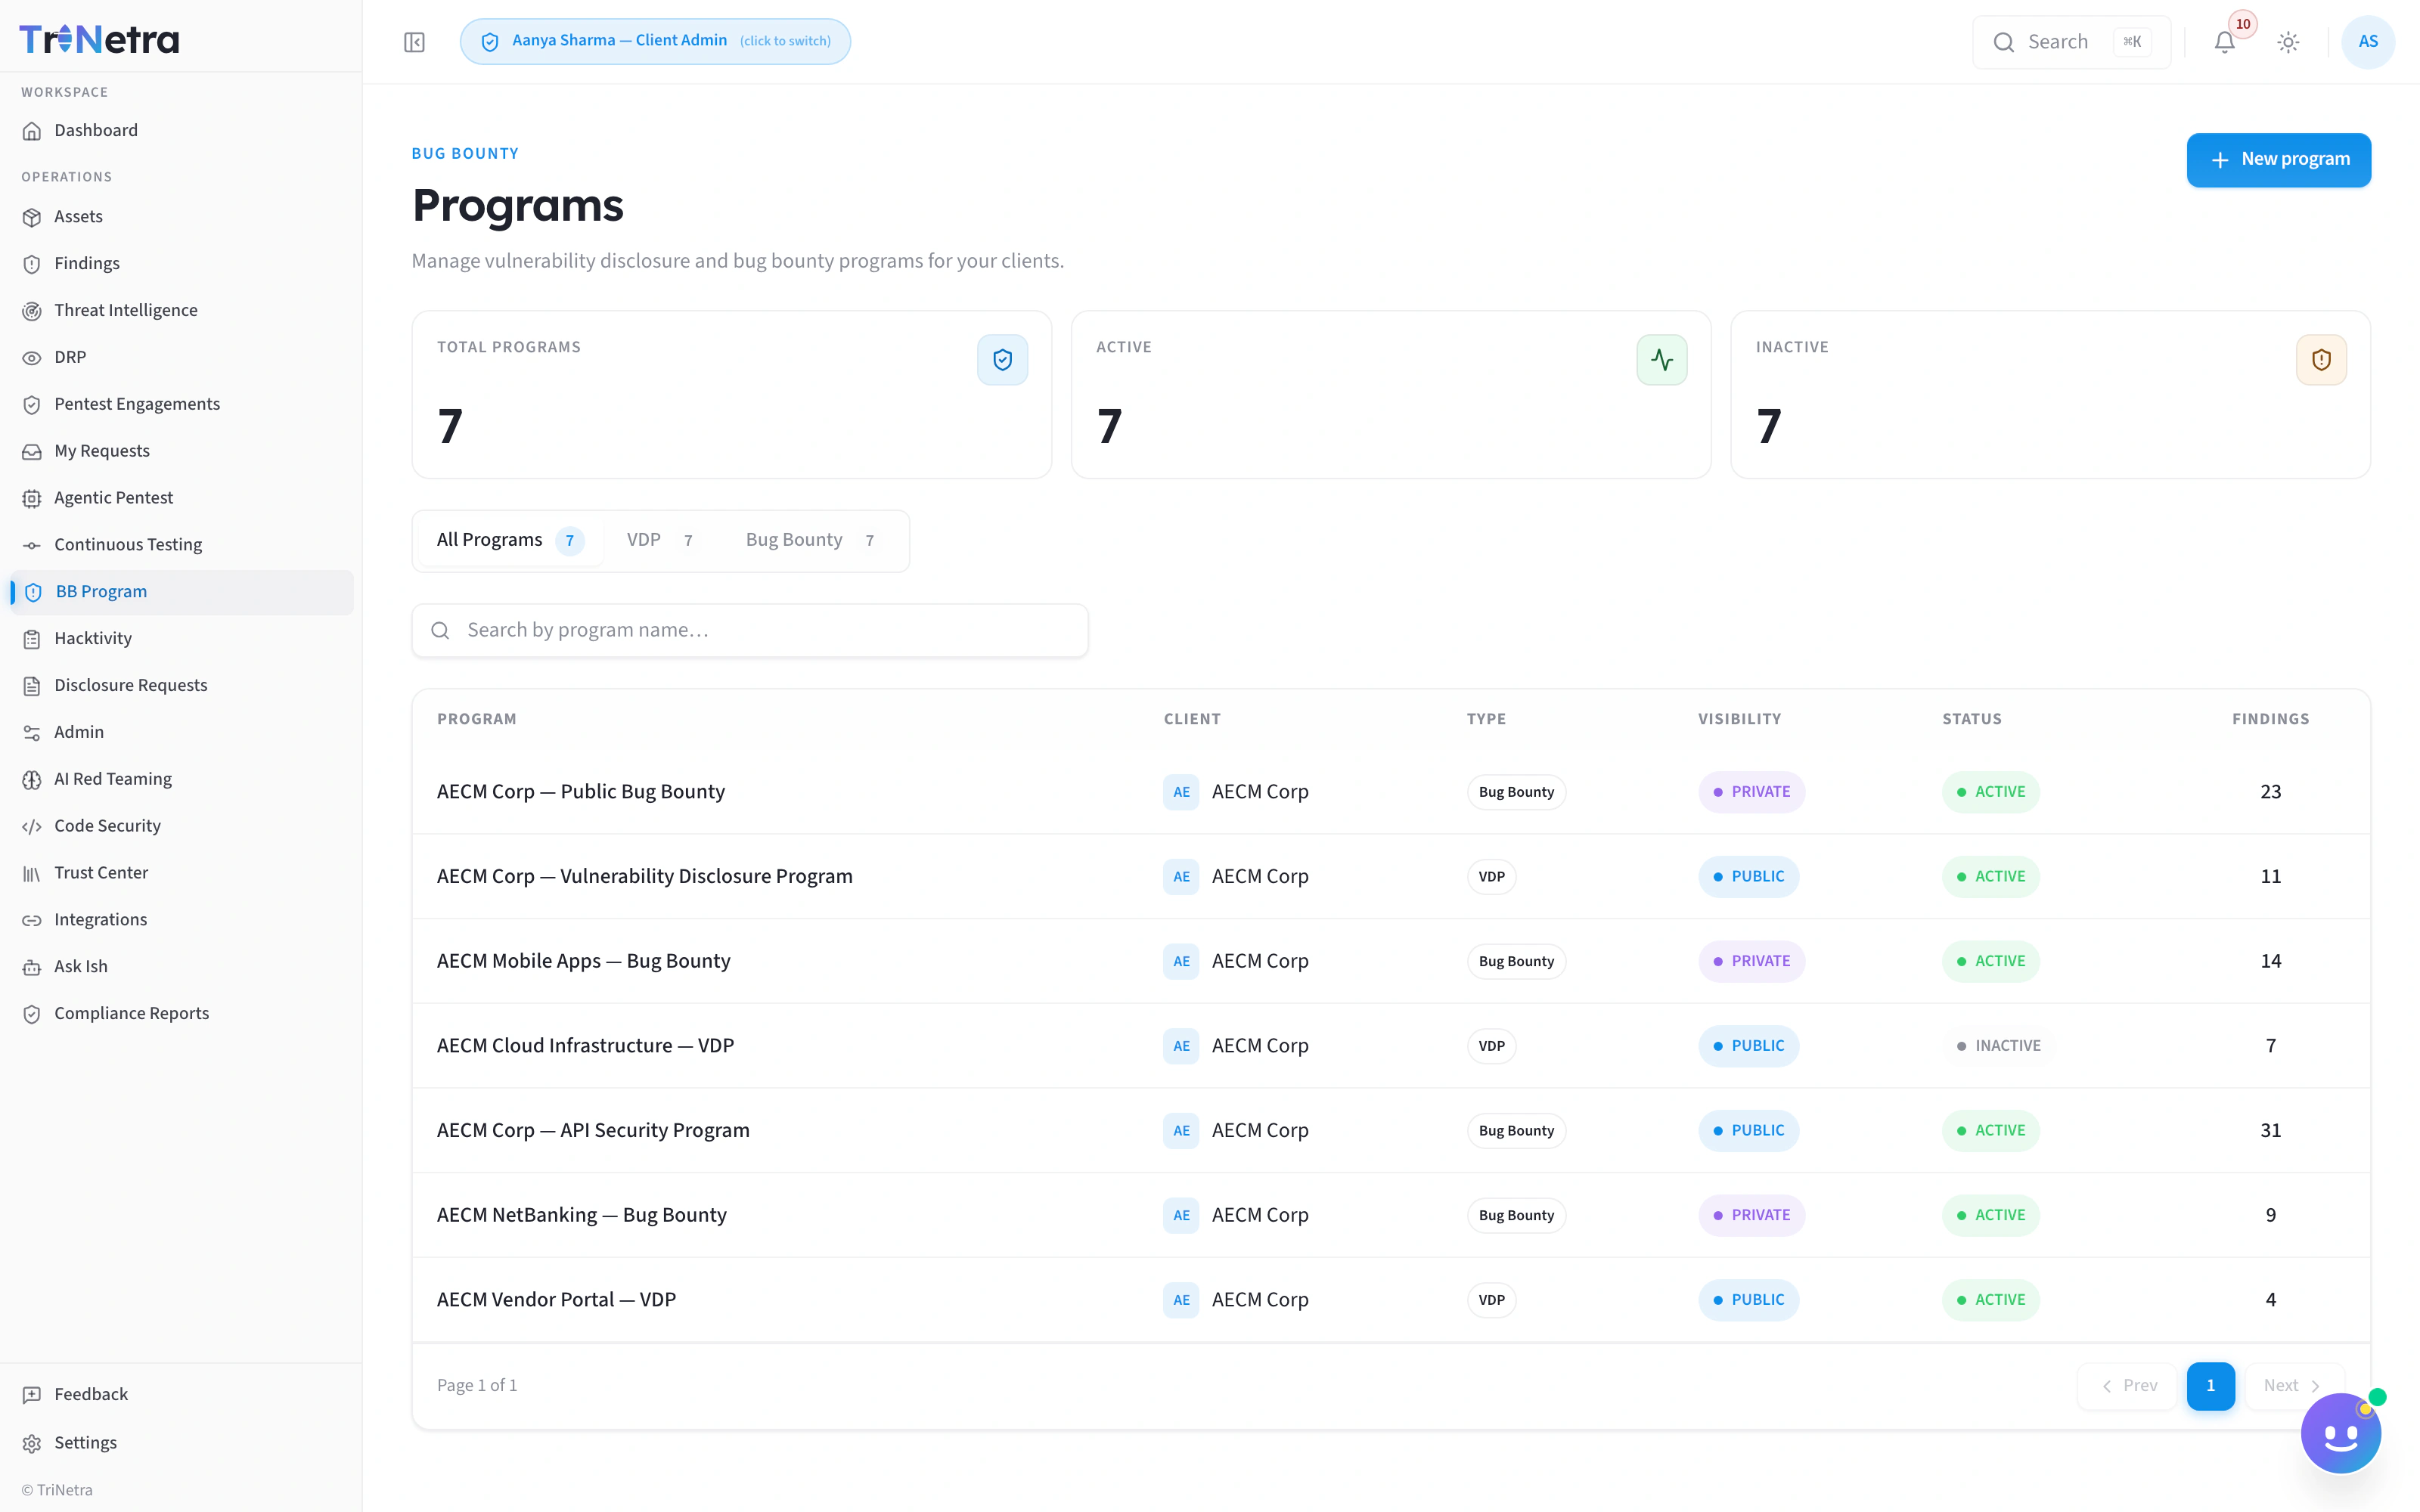
TriNetra's Bug Bounty module was built around a simple idea: the researcher experience is the program quality. Sloppy triage, silent rejections, and payout limbo drive good hunters away — so we engineered them out.
Fair, fast triage
Payouts on rails
Reputation that compounds
A profile that protects you
How it works
Five steps from application to payout.
- 01
Apply
Tell us who you are and what you hunt. One short form, and a human on the SecurityBoat team reviews every application.
- 02
Get vetted
We verify identity and review your track record. Sensitive private programs may ask for additional ID or background verification — you'll always know before you opt in.
- 03
Get invited
Once vetted, invitations open up: private and public bug bounty programs matched to your skills, plus paid PTaaS engagements you can bid on through TriNetra's researcher marketplace.
- 04
Submit
Report findings straight into the platform: steps to reproduce, evidence, severity. Triage is transparent — duplicates and severity calls are grounded in program history and confirmed by humans.
- 05
Get paid
Accepted findings resolve their reward from the program's severity tiers and flow through the payout pipeline automatically — approval, verified transfer, tracking, invoice. Reputation points land on the leaderboard at the same time.
The work
Programs, engagements, and disclosure — one platform.
Bug bounty programs
Pentest engagements
Coordinated disclosure
What you earn
Real payouts, not points-only theater.
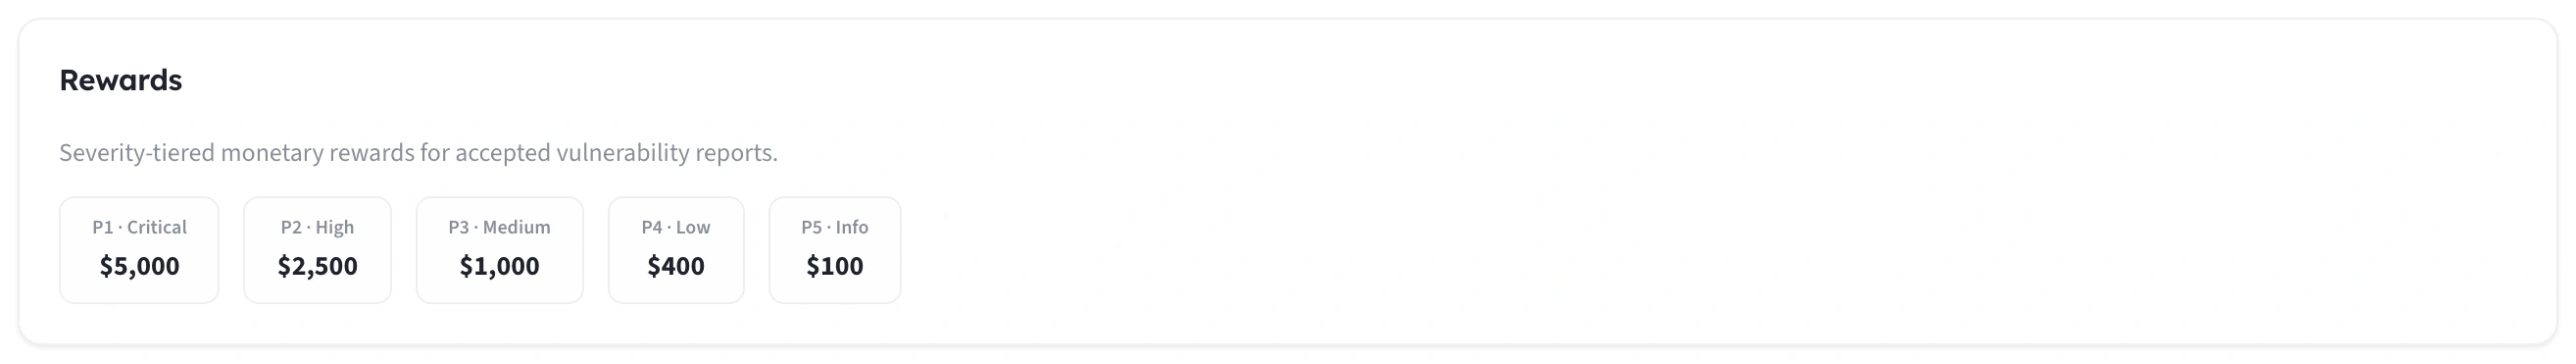
Bug Bounty programs pay per-severity reward tiers in INR or USD once a submission clears validation. VDP programs earn reputation on the same platform — points that build the rank programs recognize publicly.
Community
The hunt is here. The community is bigger.
Meetups, city chapters, talks, CTFs, and the people behind the handles — SecurityBoat's researcher community lives independently at securityboat.community.
Where to go next
See the marketplace mechanics, in detail.
Apply to hunt
Ready when you are.
One form. A human on the SecurityBoat team reviews every application by hand.
| Field | Required? | Notes |
|---|---|---|
| Full name | Required | Never shown publicly — profiles use your display name. |
| Required | Where your decision lands. | |
| Username | Required | Your public handle on programs and leaderboards. |
| Optional | Link your professional profile if you'd like. | |
| Years of experience | Required | From under a year to 5+. |
| Skills | Required (pick at least one) | Web · API · Mobile · Cloud · Network & Infrastructure · AI/LLM · Code Review · Hardware/IoT. |
We use this information only to review your application and manage your researcher account. Public profiles are PII-safe by design.
Start where the programs are.
Public programs are open now — no application needed to look.
Or explore Opportunities and the Leaderboard.