TriNetra Platform · Exposure & Risk
Catch the fakes before your customers do.
Phishing clones, typosquats, leaked credentials, impersonated executives — the threats that never touch an asset you own. TriNetra DRP watches for them around the clock across seven alert categories, backs every alert with evidence, and drives takedowns through to confirmed removal.
The problem
Your real exposure doesn't stop at your firewall. Attackers register lookalike domains, clone your pages pixel for pixel, publish fake mobile apps, sell your customers' credentials, and impersonate your executives — all without touching a single asset you own. None of it appears in an attack-surface scan, because it isn't your infrastructure. It's the landscape around it, and it's usually live for days before anyone notices.
How Digital Risk Protection answers it
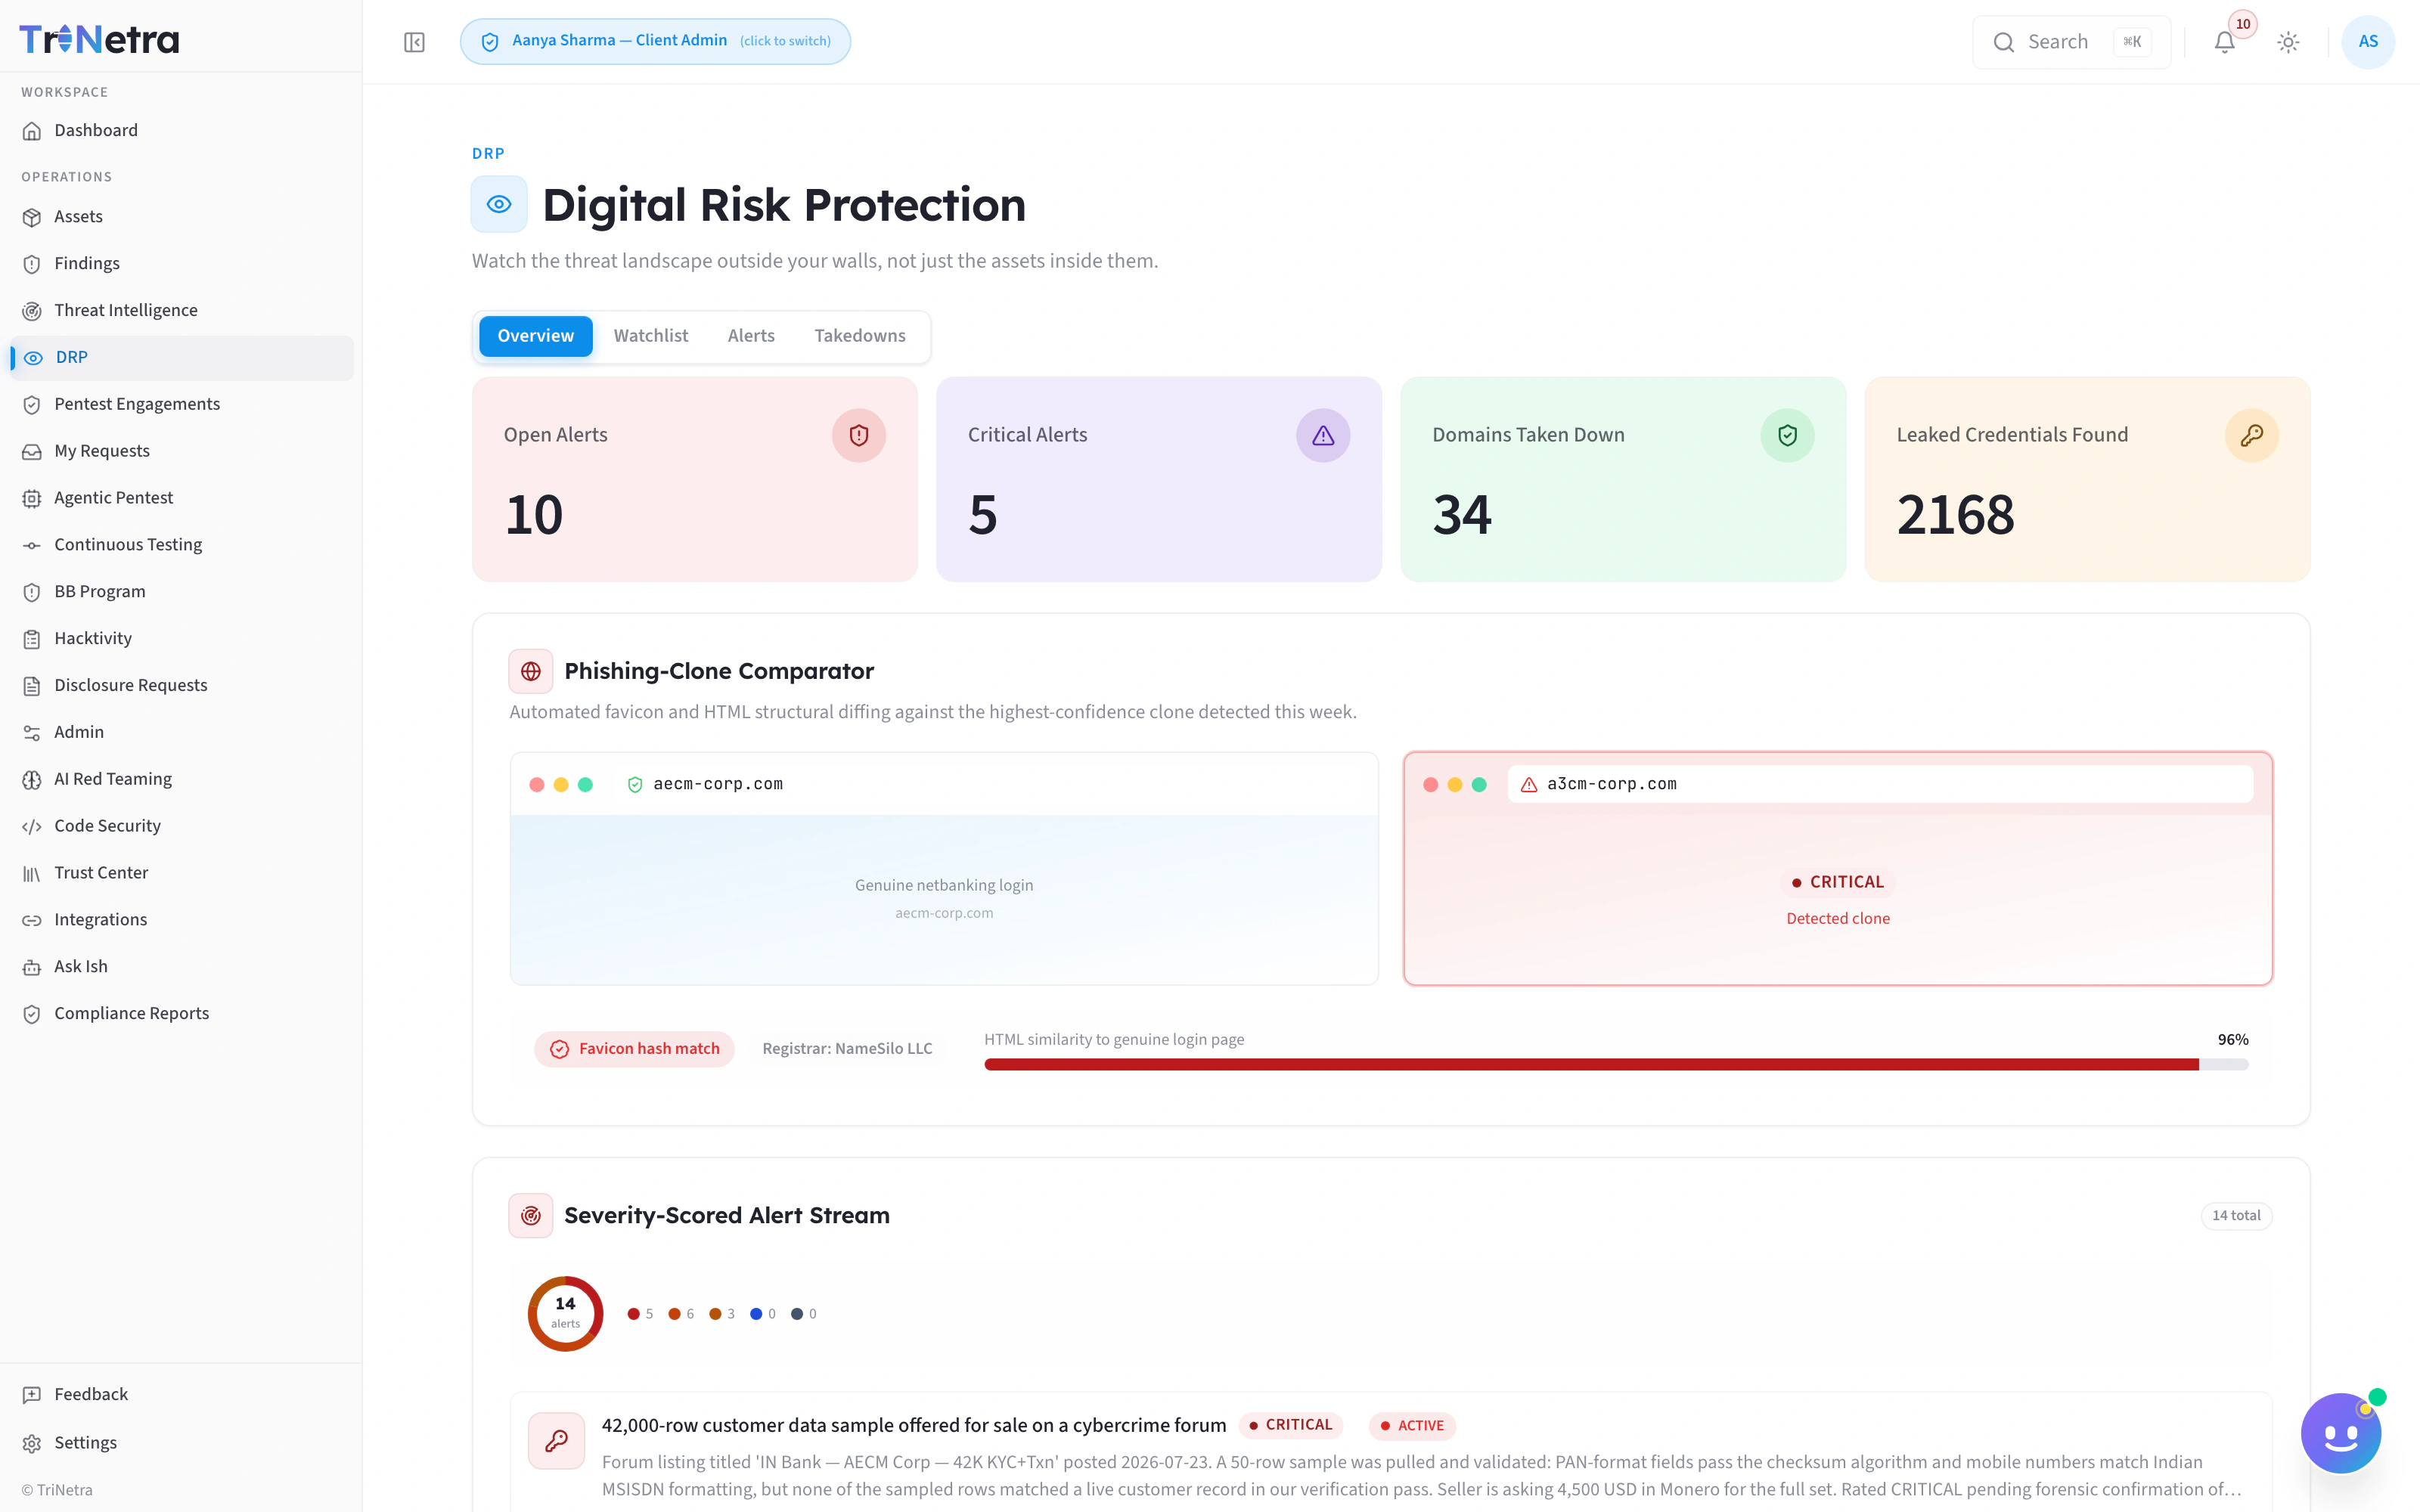
DRP monitors that landscape continuously against a watchlist you define — brand terms, domains, products, executives. Every detection lands as one of seven alert categories, severity-scored and carrying verifiable evidence: matched domain, favicon hash, HTML-similarity score, DNS records. Confirmed threats move through a takedown board from Detect to Confirm, with days-in-stage visible at every step — and the KPIs that matter, domains taken down and leaked credentials found, tracked on the dashboard.
How it works
The workflow, end to end
- 01
Build the watchlist
Define what DRP protects: brand terms, domains, product names, and executive identifiers. Every downstream detector is driven by this list.
- 02
Monitor continuously
Always-on monitors sweep for brand threats — running both standalone and alongside every attack-surface scan, so threats correlate to your real exposed footprint.
- 03
Correlate & validate
Raw hits are matched against the watchlist and enriched — WHOIS, DNS resolution, favicon fingerprinting, HTML-structure comparison — separating genuine threats from noise.
- 04
Score & alert
Every validated threat lands as one of seven categories — Phishing Clone, Typosquat/New Domain, Financial Fraud, Ransomware Leak Site, Credential Leak, Fake Mobile App, Executive Impersonation — deduplicated, severity-scored, and org-scoped.
- 05
Take it down
Actionable threats move across the takedown board — Detect → Validate → Action → Confirm — with days-in-stage on every card, so nothing stalls quietly.
- 06
Watch for re-emergence
Taken-down threats stay monitored for mirror sites and re-registration, so the same attack can't quietly resurface a week later.
Capabilities
What ships in the box
Seven alert categories
Phishing-Clone Comparator
Watchlist-driven precision
Takedown board with days-in-stage
Financial-fraud detection, built for India
Credential and extortion exposure
The KPIs leadership asks about
Inside the product
What you actually see
Works with
Stronger together
Attack Surface Management
Continuous Controls Validation
Ish
FAQ
Common questions
How is DRP different from ASM?
ASM maps and monitors infrastructure you own. DRP watches everything you don't — lookalike domains, cloned pages, fake apps, leak sites, impersonation. They're complementary by design, and TriNetra correlates the two so a brand threat is read against your real exposed footprint.
Do you handle takedowns, or just alert us?
Both. Actionable threats enter a Detect → Validate → Action → Confirm workflow with days-in-stage visible on every card and a full audit trail through confirmation. After a takedown, re-emergence monitoring watches for mirror sites and re-registration by the same actor.
What evidence comes with an alert?
Every alert carries verifiable proof: the matched domain, favicon-hash match, HTML-similarity percentage, DNS records, and — for leak-site and breach alerts — threat group, post date, and exposed-field types. Enough to act on, and enough to hand to a registrar or regulator.
Are leaked credentials shown in plaintext?
No. DRP surfaces the breach name, date, and which field types were exposed — the underlying values stay encrypted. Your team learns what's out there without the platform becoming another copy of the leak.
Find out what's already impersonating you.
Give us your brand terms and domains. We'll show you what TriNetra DRP is seeing across all seven alert categories — evidence included — within days.
Related: Attack Surface Management · Continuous Controls Validation · Ish