Compliance, powered by TriNetra
Get audit-ready. Stay audit-ready.
In India, the cost of a failed audit is rarely just a fine. A bank found short on RBI's framework can face board supersession and a mandated remediation timeline; a broker or AMC that misses SEBI's CSCRF obligations risks trading restrictions; an insurer out of step with IRDAI's cyber guidelines can have its ISNP filings frozen. Regulators here don't lead with “you got breached” — they lead with “you're not compliant, and here's what stops until you are.”
TriNetra is CERT-In empanelled — the load-bearing credential for regulated VAPT work in India, the qualifying badge SEBI, IRDAI, and RBI-regulated entities look for before they'll accept your report. Every framework page below is written from that vantage point: what the regulator specifically demands, and which real TriNetra module produces the evidence that satisfies it.
- RBI Cyber Security FrameworkAnnual Assessment 2026PENDING REVIEWReviewView
- ISO/IEC 27001:2022Annual Assessment 2026PENDING REVIEWReviewView
- SOC 2 Type IIAnnual Assessment 2026PENDING REVIEWReviewView
- IRDAI Information & Cyber SecurityAnnual Assessment 2026PENDING REVIEWReviewView
- SEBI Cyber Security & Cyber ResilienceAnnual Assessment 2026PENDING REVIEWReviewView
- ISO/IEC 27001:2022 Cloud AddendumAnnual Assessment 2026PENDING REVIEWReviewView
The shift
Compliance used to be a filing cabinet. Now it's a data feed.
Two real modules do the work behind every framework page on this hub. Continuous Controls Validation defines a control once — MFA on admin accounts, encryption at rest, access review cadence — and maps it to every framework it satisfies at once, so proving a control to SOC 2 also satisfies ISO 27001, HIPAA, or a client questionnaire without re-proving it separately. Today CCV ships as regulatory VAPT compliance reporting: SEBI CSCRF and IRDAI report generation end-to-end, with findings, severity matrices, scope tables, and methodology checklists auto-aggregated from real pentest engagement data, approval-gated so clients only ever see a reviewed report.
Continuous Controls Validation
PTaaS
Attack Surface Management
Trust Center
Ish, TriNetra's AI analyst, reads across all of it — ask which open findings would block your next submission and get an answer grounded in your live data.
Indian Regulatory
Built for regulated India, first.
SecurityBoat is CERT-In empanelled and works inside India's regulatory calendar every day — RBI supervision cycles, SEBI CSCRF submissions, IRDAI audits. TriNetra ships with Indian regulatory report formats as first-class citizens, not templates bolted on later.
CERT-In Security Audit
RBI Cybersecurity Framework
RBI Payment Aggregator (PA-PG) Audit
SEBI CSCRF
IRDAI Cybersecurity
NPCI / UPI Compliance
UIDAI AUA-KUA Audit
SBI VSCC Audit
ATM & POS Security Audit
NSE Trading Member VAPT
SAR / Data Localization
International & Privacy
Ready for the world.
The same evidence engine covers the frameworks your global customers and auditors expect. Prove a control once; let it count everywhere it applies.
PCI DSS v4.0
ISO 27001
SOC 2
HIPAA
GDPR
DPDP Act
IEC 62443 (Industrial/OT)
MAS TRM (Singapore)
Related · Vendor Risk Assessment
Your regulators hold you accountable for your vendors. So should your evidence.
A self-attested spreadsheet tells you what a vendor believes about their security. TriNetra tells you what's observable: test the connection points you actually share, see a critical vendor's internet-facing exposure the way an attacker would, catch leaked credentials tied to the domains your data flows through — then track remediation commitments to verified closure, on the same append-only record your own findings get.
Testing shared integrations
Outside-in vendor exposure
Vendor breach signals
Answering reviews about you
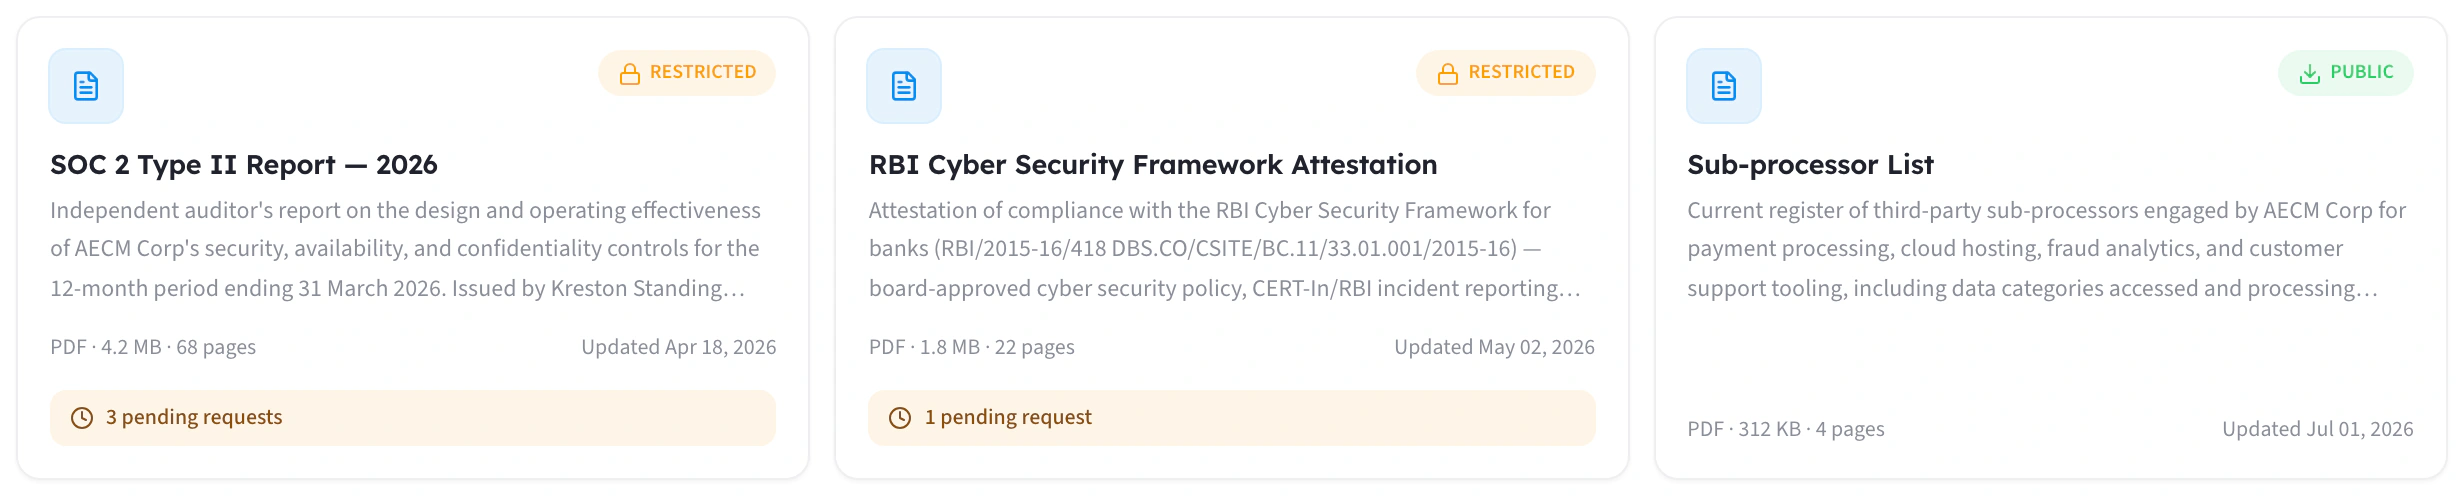
And when you're the vendor: the Trust Center turns the security reviews you receive into a self-serve experience — your pentest reports, policies, and certifications organized by category, released through an access-request approval workflow, with a full audit trail. The tenth bank asking for your audit evidence costs you an approval click, not a week.
Credentials
Audited by the audited.
SecurityBoat holds the credentials regulators and procurement teams check first: CERT-In empanelled, CREST Member, ISO 27001, ISO 9001, SOC 2 Type 2. We run our own compliance on the platform we sell you.

Not sure which framework applies to you?
Talk to a compliance-aligned pentest lead before you scope anything — tell us which regulators govern you, and we'll show you, on live platform data, exactly which modules produce the evidence each one asks for.
Let's Connect