The platform, by SecurityBoat
One platform. Eleven ways to see.
Every TriNetra module shares one lens: AI agents discover and test continuously, vetted humans validate what's real, and every result lands in a single governed record — from first discovery to verified fix.
Three slices of the lens
Discover. Validate. Govern.
Point tools see fragments. TriNetra's modules are organized around the three things a security program actually has to do — and they work one shared record, not eleven silos.
Discover
Exposure & Risk
ASM maps every asset you own — including ones you forgot. DRP watches for phishing clones, leaked credentials, and brand impersonation.
Validate
Offensive Testing
PTaaS, Bug Bounty, Agentic Pentest, Continuous Testing, AI Red Teaming, Code Security — proof over noise: only exploitable, human-verified findings reach your team.
Govern
Governance & Trust
Continuous Controls Validation, compliance-mapped reports (IRDAI, SEBI CSCRF, RBI, SOC 2, ISO 27001), and a Trust Center to share evidence securely.
Ish — the layer above every module
Ask one question. Get an answer that spans your whole program.
Ish reads across PTaaS, ASM, Bug Bounty, DRP, Continuous Testing, AI Red Teaming, Code Security, and Compliance Reports, and answers in plain language — it does not take actions, create tickets, or execute changes on your behalf.
You
Is anything impersonating our brand right now?
Ish
DRP is currently tracking active alerts, several of them Critical. The two most urgent: a pixel-perfect netbanking clone — favicon-hash match, high HTML similarity to your real login page, with a takedown request already filed with the registrar — and your organization named on a ransomware leak-site countdown, no data posted yet. A cloned mobile banking APK is also circulating on a third-party app mirror. Want me to open the DRP takedown board?
You
What are my highest-priority findings right now?
Ish
You have open Critical and High findings across production assets. The three to tackle first, all internet-reachable: a SQL injection in a legacy reporting export, an authentication bypass on an admin API, and an AWS access key exposed in a public JS bundle. Given your PCI scope, I'd start with the SQLi. Want me to open the Findings list filtered to Critical?
Every answer above carries a model badge and token count in-product — a small, honest signal that Ish is a swappable, auditable reasoning layer, not a black box.
The modules
Eleven modules, four clusters, one record.
Start with one, add the rest as your program grows — every module you switch on deepens the same picture.
Cross-platform
The analyst layer — one prompt that reads across every module below.
Offensive Testing
Proof over noise: exploitable, human-verified findings only.
Bug Bounty
PTaaS
Agentic Pentest
Continuous Testing
AI Red Teaming
Code Security
Exposure & Risk
Know what you expose before someone else maps it for you.
Governance & Trust
Controls tested on a cadence, and the resulting evidence shared on your terms.
One governed record
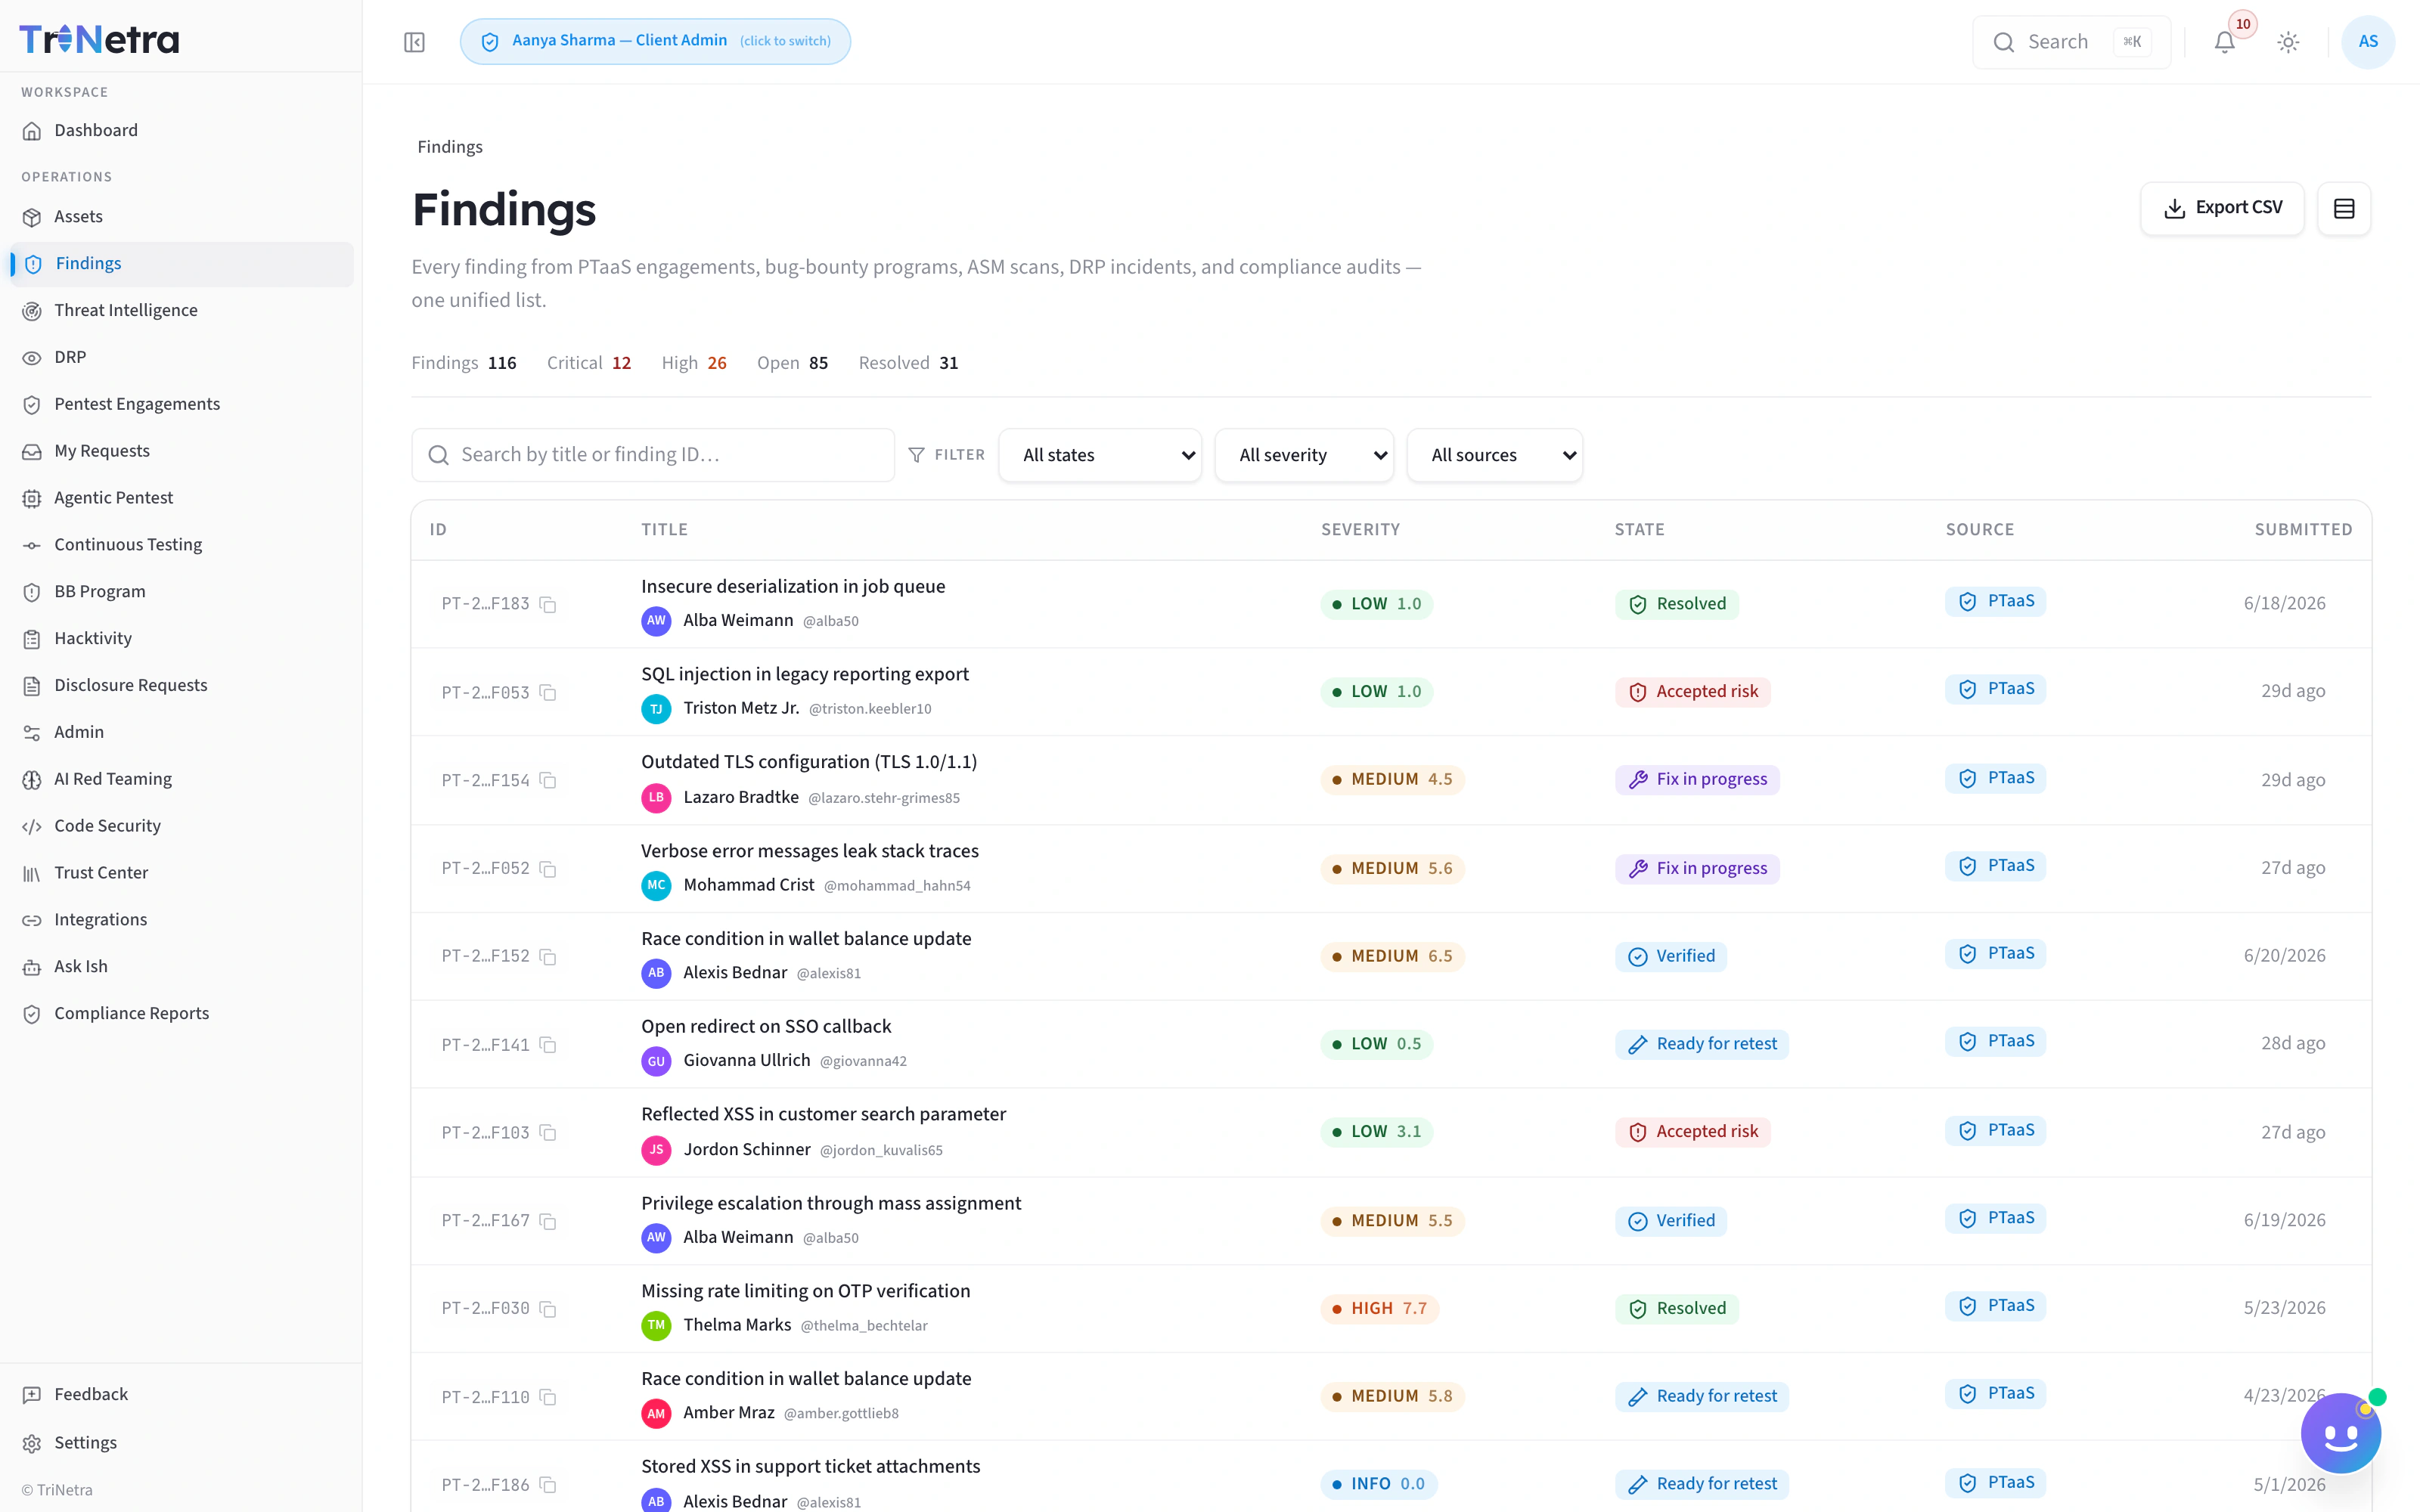
Every finding, one list, one truth.
Every finding from PTaaS, bug bounty, ASM, DRP, and compliance lands in one governed list — severity-scored, owner-assigned, and tracked from first report to verified fix. No more reconciling five tools to answer “are we exposed?”
Integrations
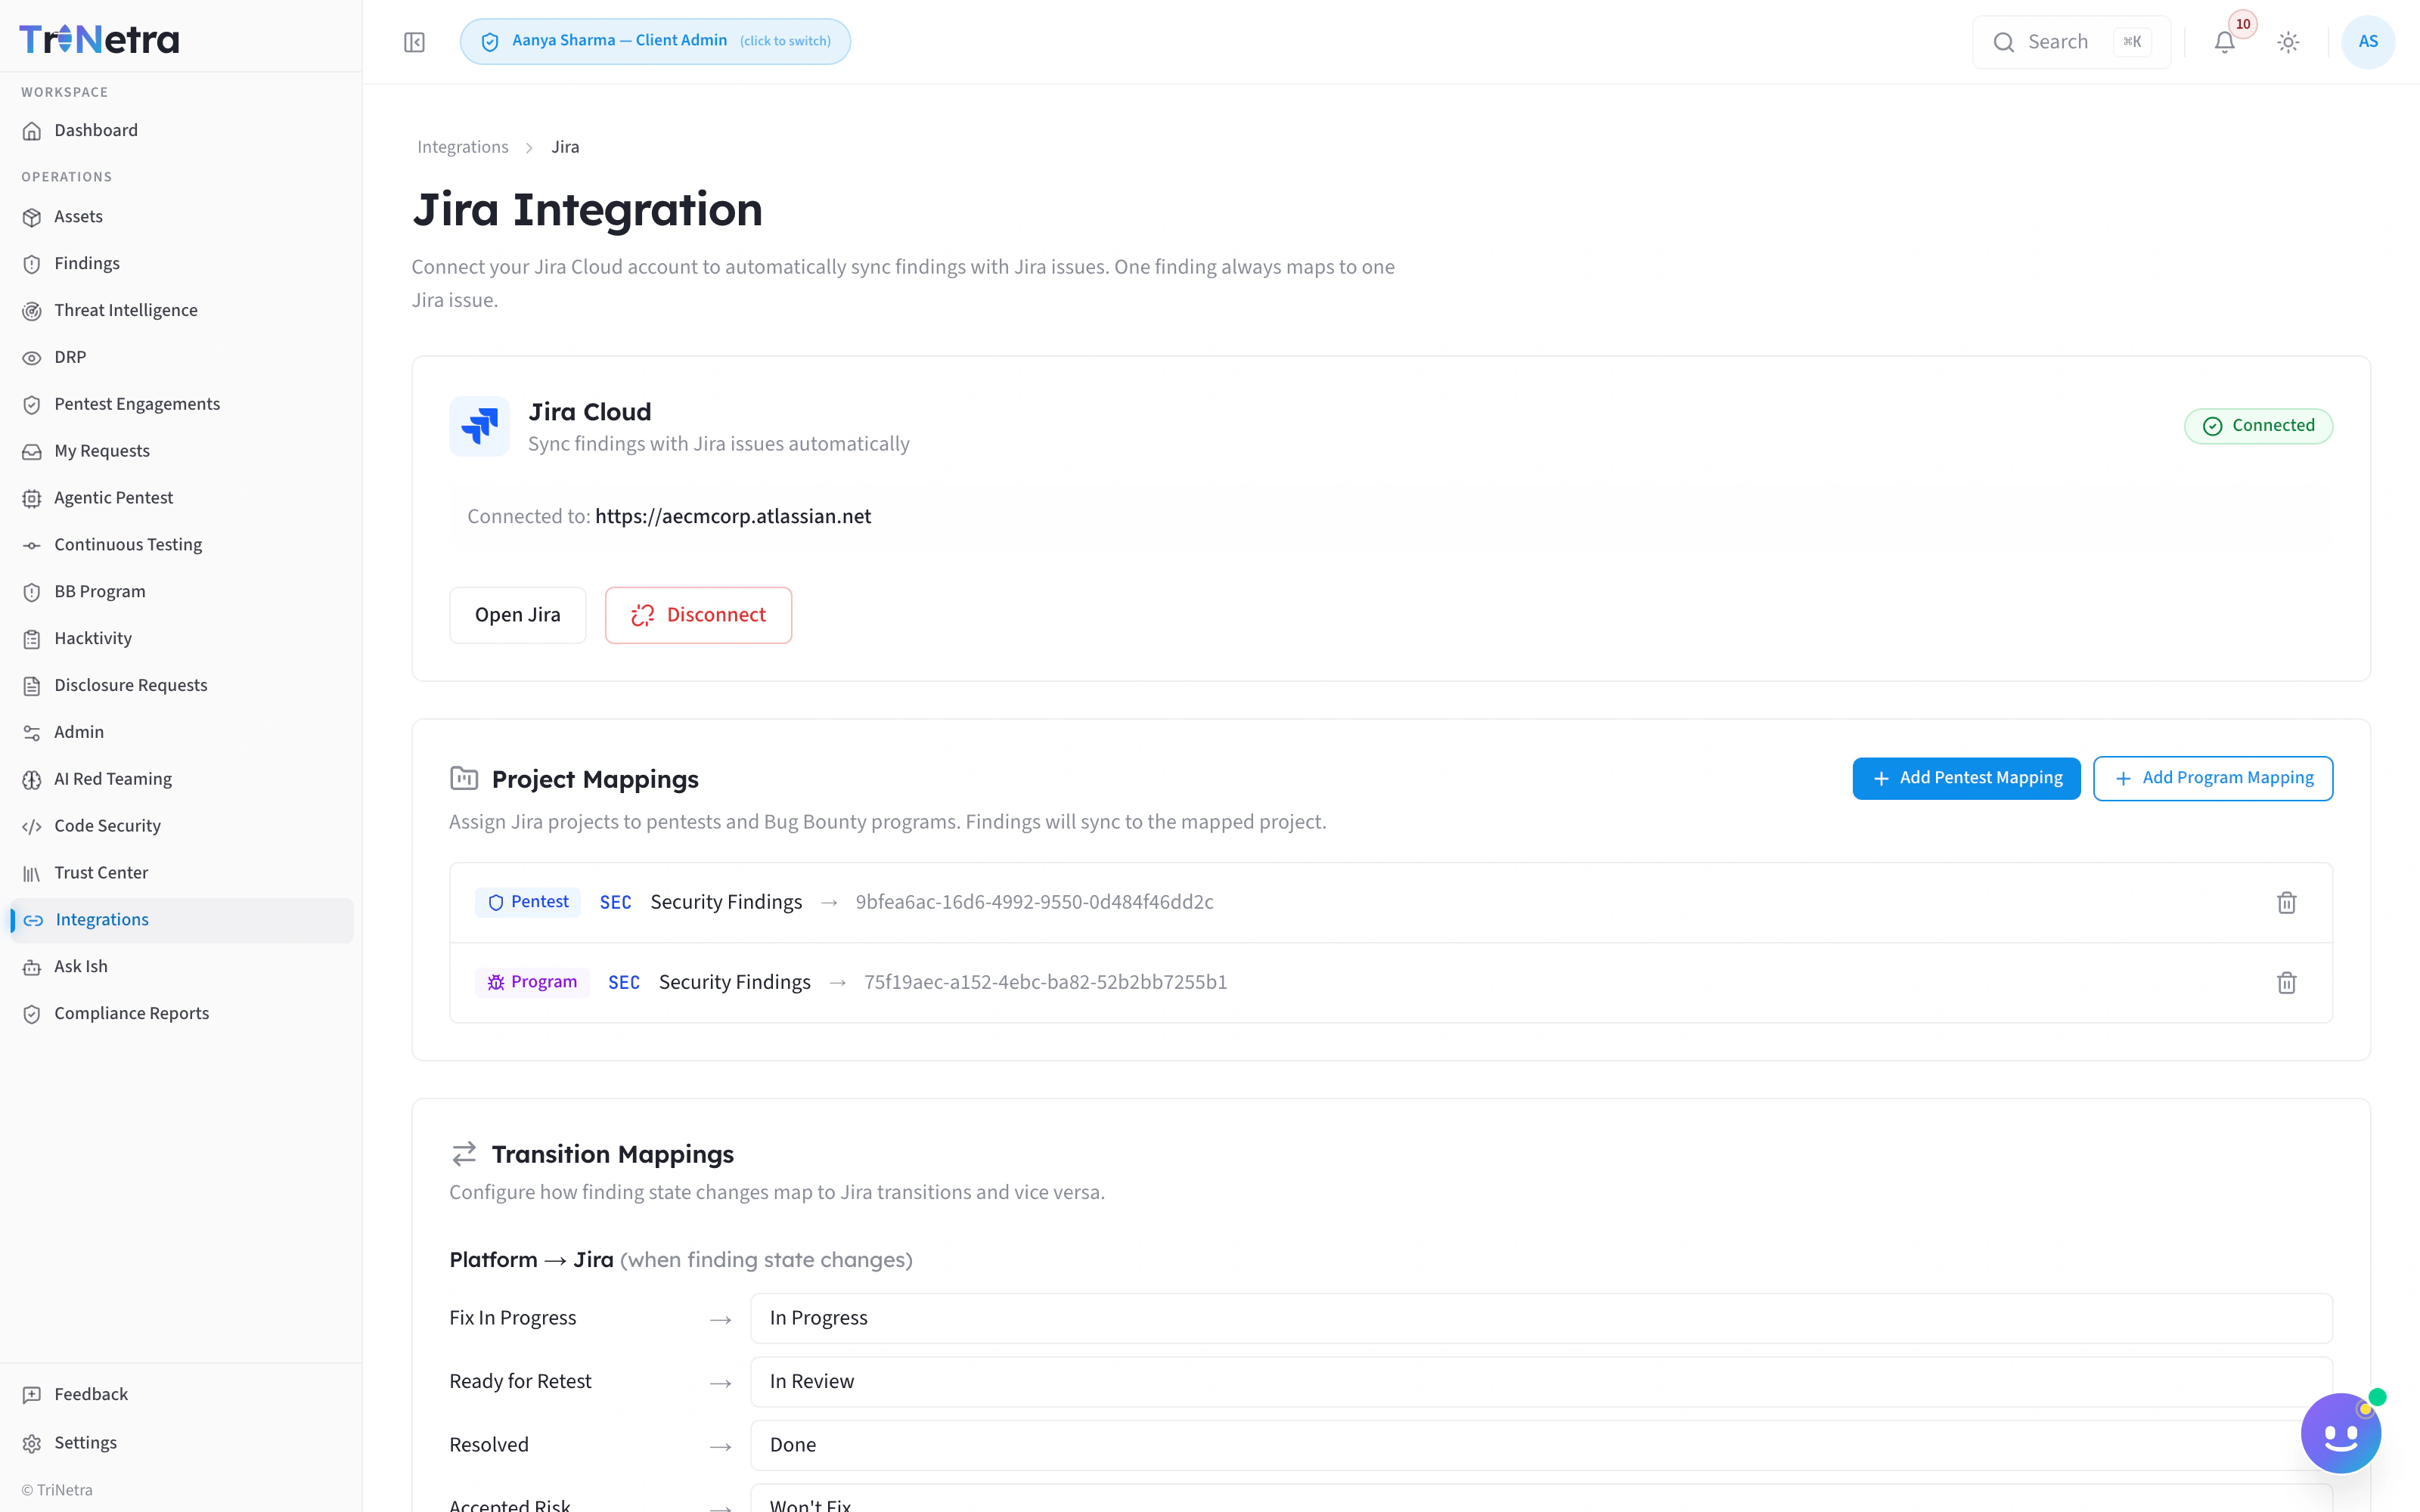
Findings go where your team already works.
Two-way Jira sync is live today: a validated finding becomes a ticket with severity, evidence, and owner attached — and when your team resolves it, TriNetra knows and queues the retest.
Beyond the platform
Humans for the moments that need them.
The platform runs continuously — and when you need senior judgment rather than another dashboard, SecurityBoat's team steps in. Both are service engagements — priced, scoped, and delivered by SecurityBoat's own team, not self-serve modules.
vCISO as a Service
Incident Response
See all eleven angles — on your scope, not a demo.
Tell us what you're protecting. We'll show you what TriNetra sees — discovery, findings, and reporting, live.
Let's Connect